Meet the TDR team
Stationed on Sekoia’s frontlines, we’re a force of a threat researchers and analysts on a mission to track state-sponsored actors and dismantle cybercrime networks.
Our 4 pillars of expertise

Strategic analysis
“We provide the strategic and geopolitical context around cyber threats to explain adversaries’ motivations and better understand the threat landscape.”
Threat tracking
“We develop our tools and methodologies to hunt new threats and proactively track known ones.”
Detection and hunting
“We develop high-quality Sigma rules to detect the most common TTPs and avoid false positives as far as possible.”
Reverse engineering
“We analyse malicious code and malware to better understand, track and detect it, and thus protect our customers.”
What we focus on
We go far beyond the alerts, turning complex data into the intelligence and rules needed to power your defense.
Provide actionable intelligence
Deliver up-to-date, contextualized, and verified IoCs.
Focus on investigations
Invest in emerging threats and the most active current threats.
Enrich open-source publications
Offer exclusive indicators to our customers.
Create new detection rules
Advance our threat detection capabilities to identify complex attacker tactics, techniques, and procedures (TTPs).
Contextualize everything
Employ Kill Chain, ATT&CK, STIX modelisation, IOC livetime, and more.
Share with the community
Share our research with high-quality private and public reports.
The TDR team in numbers
From thousands of custom rules to millions of intel objects, we provide the raw power behind the Sekoia SOC platform.
10M+
Stix Objects
<0.015%
False positive rate
1000+
Detection rules
5000+
Enriched reports
Read the latest by TDR team
We turn our daily investigations into actionable intelligence that anyone can use. Take a look at our latest research to stay one step ahead.
Poisoned Source: APT29 watering holes target mobile devices with n-day exploits
Sekoia TDR investigates a large-scale APT29 watering hole campaign targeting iOS and Android users through compromised websites, fake domains, and a supply-chain attack. Discover how n-day exploits were used to steal cookies, Wi-Fi passwords, and device data.
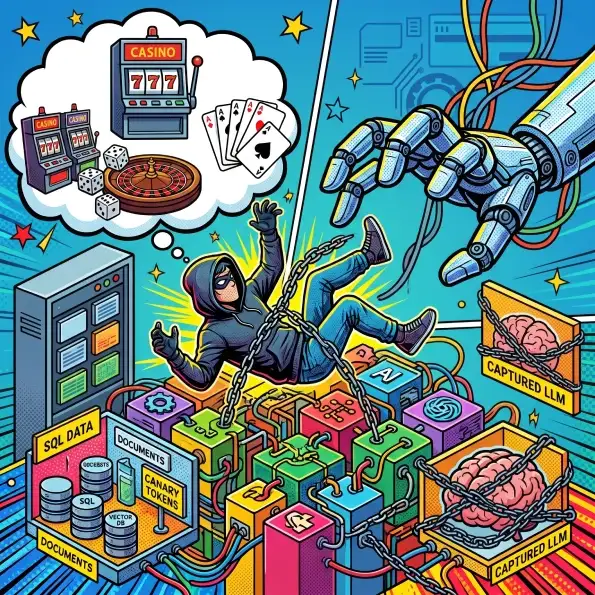
A honeypot's tale: Deconstructing an attack on GenAI infrastructure
Sekoia's TDR team ran a decoy Flowise server to study attacks on GenAI platforms. One threat actor stole its credentials and tried to misuse its AI agent.

Gotta breach 'em all! The journey of ShinyHunters
ShinyHunters has outlasted forum takedowns, multiple arrests, and its own founders' convictions. This report traces six years of activity and tactical evolution. From stolen S3 buckets to zero-day exploits, we attempted to explain why the brand keeps surviving what should have ended it.
Our conferences
The TDR team travels the globe to share exclusive intelligence and detection strategies with fellow researchers and defenders. Take a look at our latest talks and briefings.


Sekoia in the media
Our Board of Directors include recognized investors and independent board member Guillaume Poupard, DGA of Docaposte and former GM of ANSSI.