Autonomous SOC Platform
One platform.
Total control.
Now, your SOC analysts can actually do their jobs. Only faster. Sekoia’s AI agents investigate alerts at machine speed and handle repetitive tasks, so SOC analysts can focus on decisions and response.

AN AUTONOMOUS SECURITY OPERATIONS CENTER PLATFORM
AI at the core
24/7
AI-powered threat analysis
1,500+
detections enriched with intelligence
90%
less manual triage effort
10x
faster response workflows
An autonomous SOC platform for detection, investigation, and response
Sekoia connects your SOC team, threat intelligence and security platform workflows, helping security operations teams act faster with greater clarity and confidence.
Detection agents combine anomaly detection, behavioral analytics, machine learning, and AI models to strengthen threat detection across hybrid environments and network segments.
Agentic Workflows
Unified Intelligence
Adaptive Detection Models
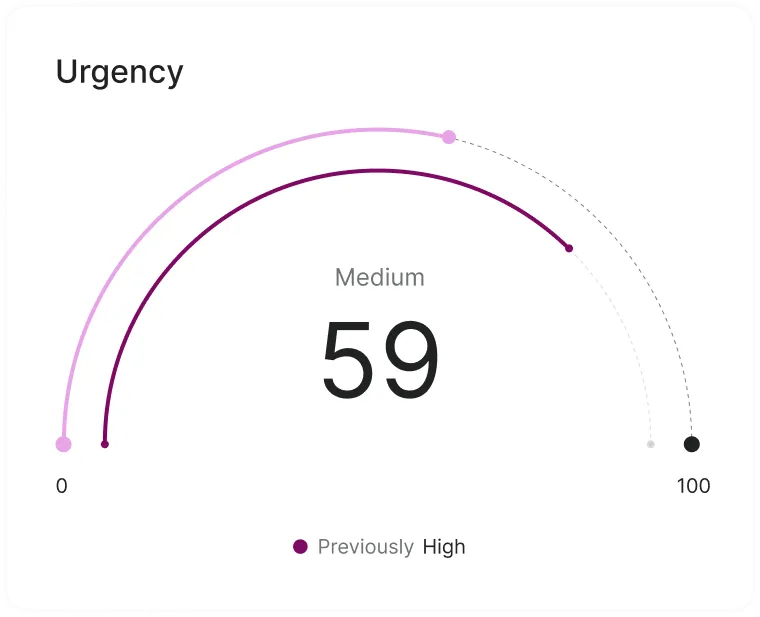
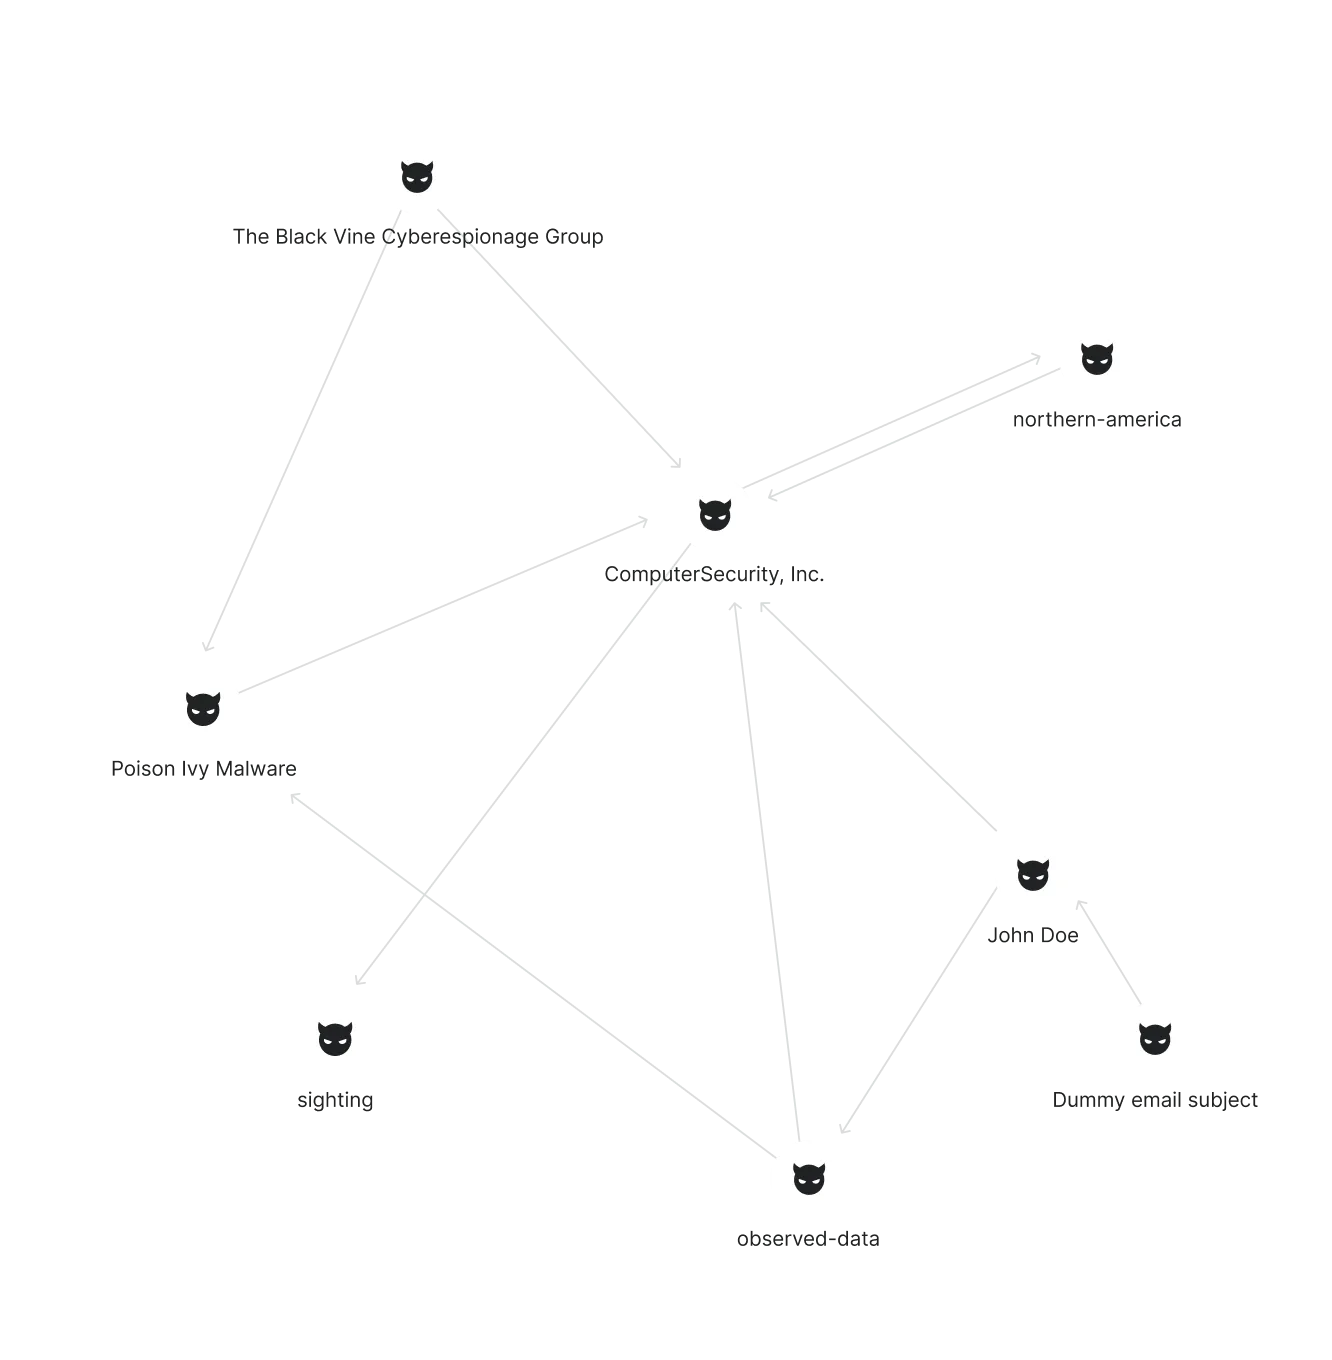
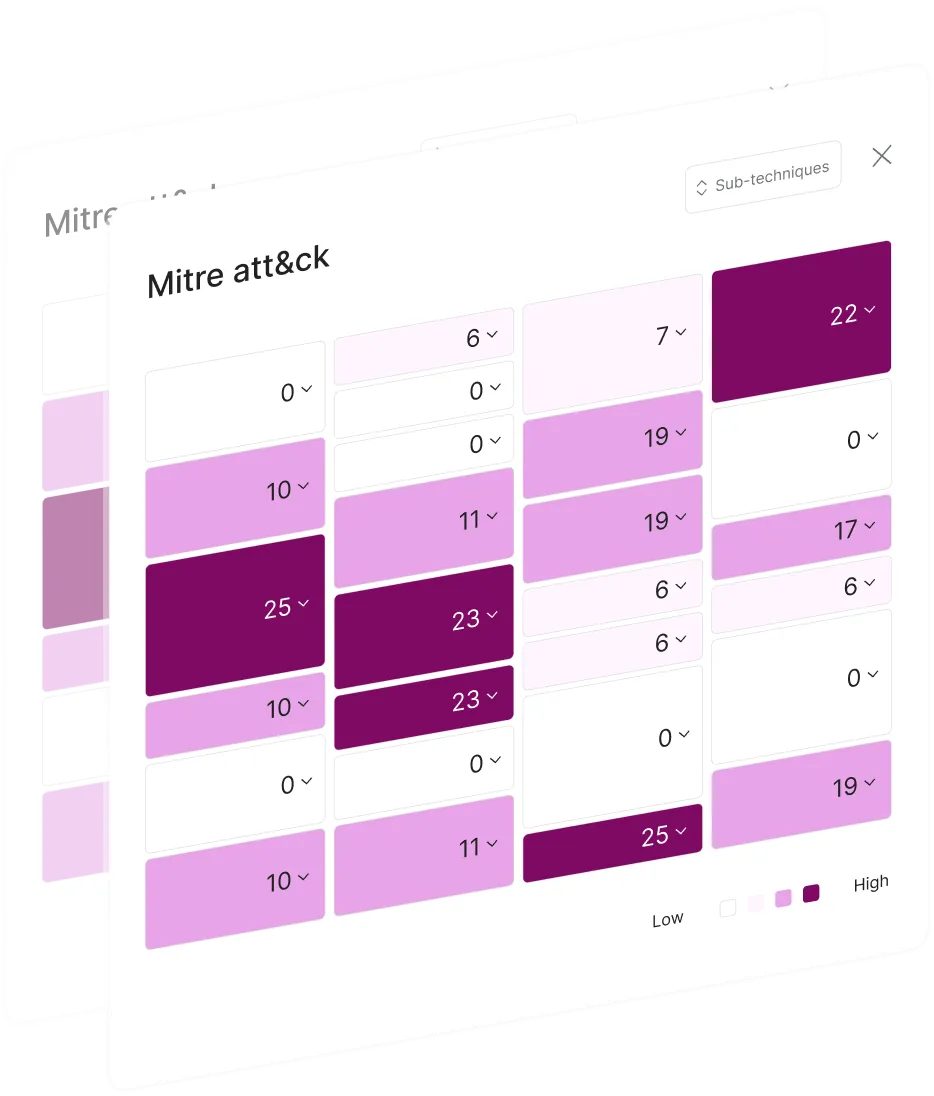

Investigate every alert with greater context. Continuous monitoring helps reduce alert fatigue and time spent chasing false positives.
Intelligence Led Threat Hunting
Fully Guided Hunts
Continuous Adversary Tracking
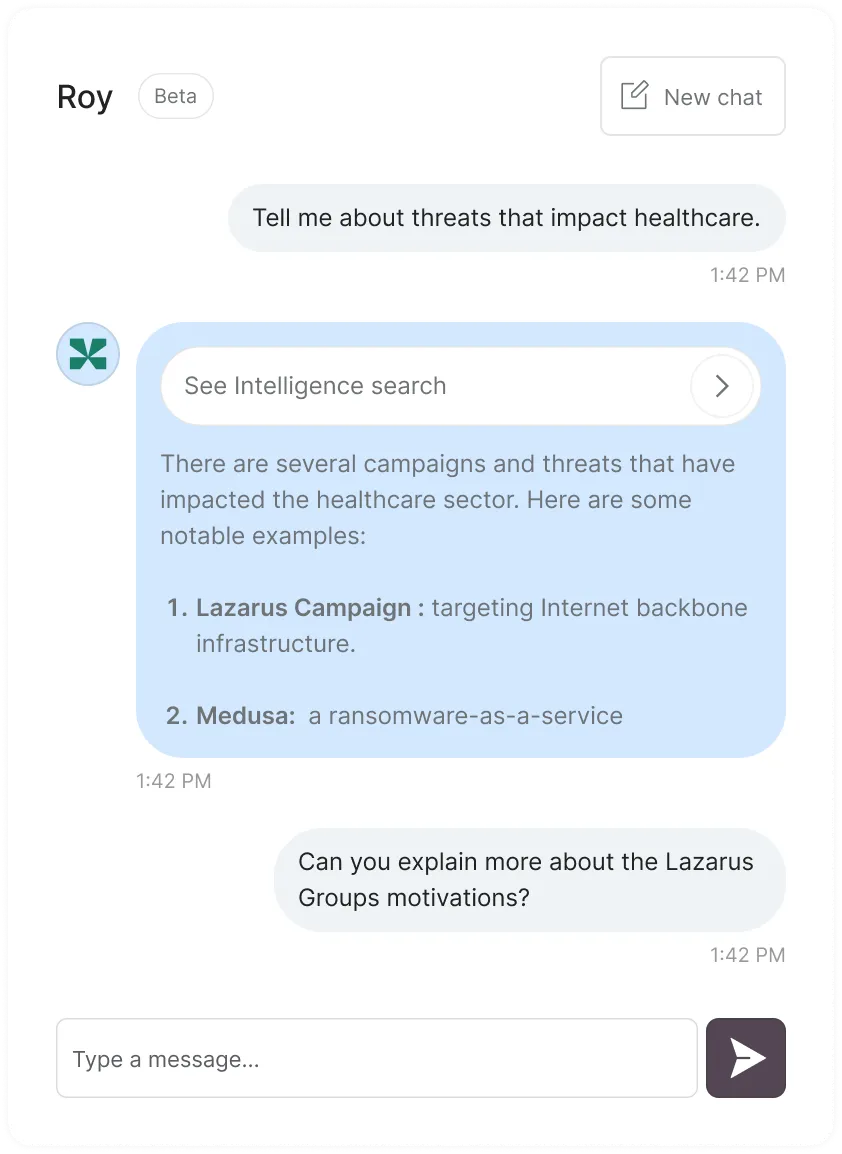
Respond to each incident with advanced analytics and AI that support incident response. Sekoia Elevate agents guide the investigation workflow.
Automated Evidence Gathering
Ask-Anything Analysis for cybersecurity operations teams
Ensure compliance and policy enforcement
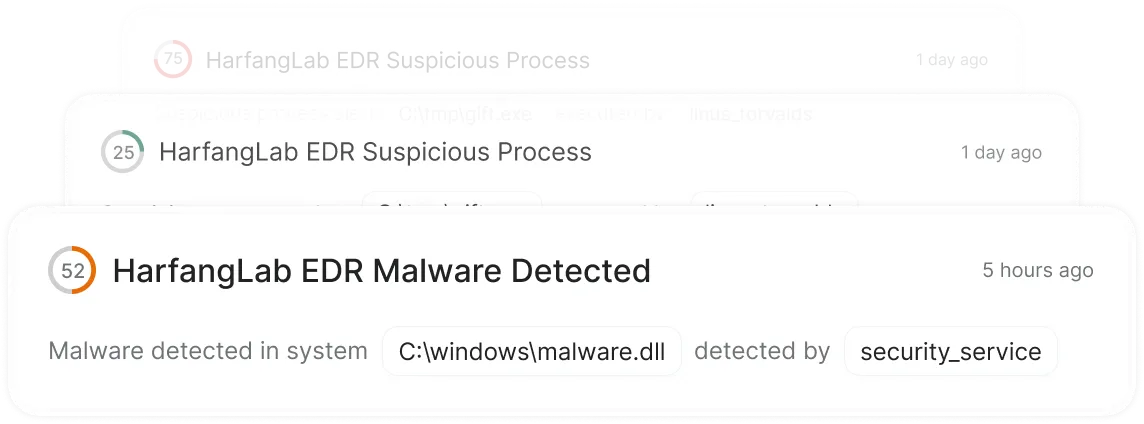
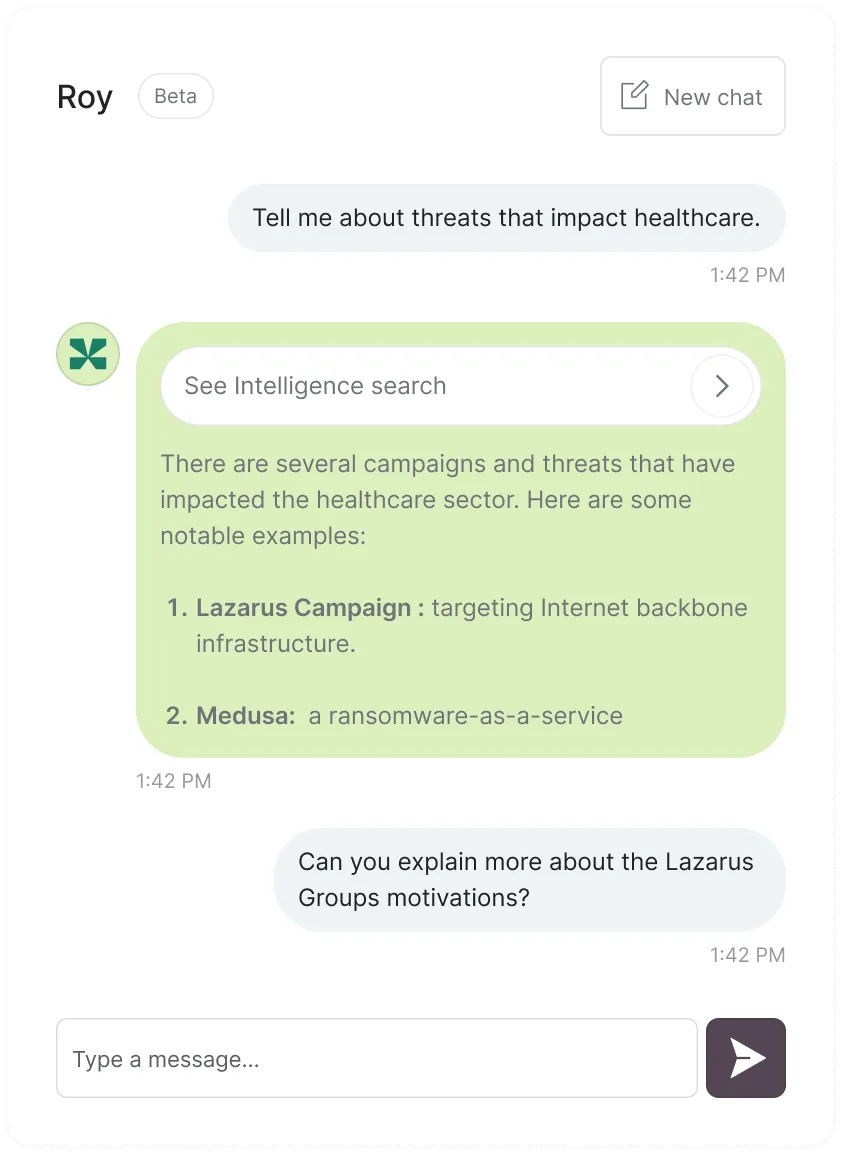
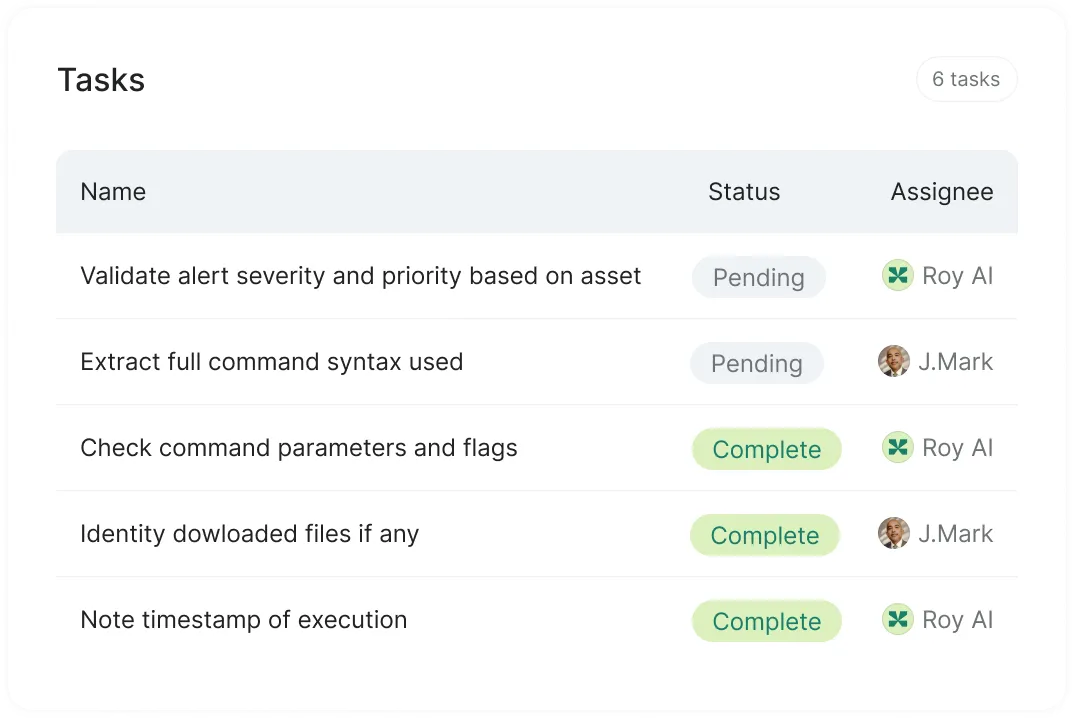
Automate response with the Sekoia autonomous SOC platform, supporting autonomous action when policies allow. Driven by Sekoia Elevate.
Playbooks that Evolve
Orchestrated Enterprise-Wide Response
Autonomous Containment security measures

“Sekoia's intuitive interface and advanced analytics capabilities have significantly enhanced our alert triage process. It also has a simple and quick integration with our existing security stack.”
Security leaders of all sizes choose Sekoia to strengthen their defenses against modern threats.
Partners rely on Sekoia to deploy faster, scale globally, and deliver protection their teams trust.
See our partner stories
AI at the core
Most security stacks force teams to stitch together disconnected tools. Sekoia brings AI agents into a single agentic SOC platform that operates across every module and your existing tooling.

AI agents that turn data
into decisions
Sekoia AI agents work across the platform to help analysts move from signal to action faster. They surface alerts, gather context, connect evidence and support AI triage and next actions. This helps teams reduce manual effort and focus on decisions that require human judgment.
Agent-orchestrated detection
AI agents turn large volumes of security data into prioritized, actionable insights as alert volume grows. By correlating signals across endpoints, networks, cloud logs, email security, identity and third-party tools, they help human SOC analysts understand what matters and accelerate triage.
Get a demo

Agent-guided investigation
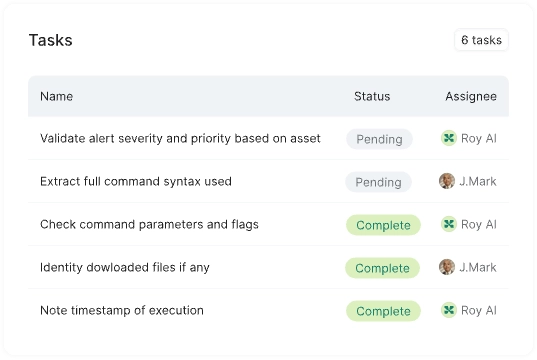
AI agents assist analysts throughout the alert investigation process by enriching alerts, summarizing relevant context, highlighting likely attack paths, and helping connect related activity. This gives teams a faster, more consistent way to investigate without relying on manual pivots across multiple tools.
Get a demo

Agent-led response
AI agents help analysts handle repetitive tasks across investigation and response workflows. They support enrichment, case preparation, notifications, and response actions, reducing the operational burden on security teams.
Get a demo
How it works
Read our latest blog articles
Poisoned Source: APT29 watering holes target mobile devices with n-day exploits
Sekoia TDR investigates a large-scale APT29 watering hole campaign targeting iOS and Android users through compromised websites, fake domains, and a supply-chain attack. Discover how n-day exploits were used to steal cookies, Wi-Fi passwords, and device data.

Resources
View all resources