Unveiling the intricacies of DiceLoader
This report aims to detail the functioning of a malware used by FIN7 since 2021, named DiceLoader (also known Icebot), and to provide a comprehensive approach of the threat by detailing the related Techniques and Procedures.
CustomerLoader: A new malware distributing a wide variety of payloads
This blog post aims at presenting a technical analysis of CustomerLoader focusing on the decryption of the next-stage payloads, an overview of more than 30 known and distributed malware families, and details on three infection chains observed distrib
Stealc: A copycat of Vidar and Raccoon infostealers gaining in popularity - Part 2
This blog post is a technical analysis of Stealc infostealer, detailing different characteristics of the malware, including anti analysis, strings de-obfuscation and C2 communication techniques.

Stealc: a copycat of Vidar and Raccoon infostealers gaining in popularity - Part 1
This blogpost aims at presenting the activities of the Stealc’s alleged developer, a technical analysis of the malware and its C2 communications, and how to track it.
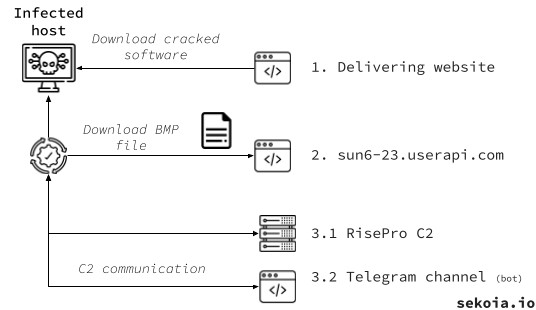

PrivateLoader: The loader of the prevalent ruzki PPI service
Sekoia analysts tracked PrivateLoader’s network infrastructure for several months and recently conducted an in-depth analysis of the malware. In parallel, we also monitored activities related to the ruzki PPI malware service.
Raccoon Stealer v2 - Part 2: In-depth analysis
This blog post is a technical analysis of the new Raccoon Stealer 2.0 stand-alone version. Authors have announced that the malware is also available in a DLL format or could be embedded in other PE.