

Scattered Spider (aka UNC3944) Laying New Eggs
This report provides an overview of the Scattered Spider evolution, its modus operandi and the toolset leveraged over the past years. Additionally, it delves into the Scattered Spider TTPs, as well as the latest ongoing campaigns.

Adversary infrastructures tracked in 2023
Sekoia.io C2 Trackers identified more than 85,000 IP addresses used as C2 servers in 2023, an increase of more than 30% compared to 2022.
Unveiling the intricacies of DiceLoader
This report aims to detail the functioning of a malware used by FIN7 since 2021, named DiceLoader (also known Icebot), and to provide a comprehensive approach of the threat by detailing the related Techniques and Procedures.
Securing gold: Assessing cyber threats during Paris 2024
Based on these observations and given the constantly evolving cyber threat landscape, we analysed cyber threats affecting previous editions of the Olympics, as well as the current geopolitical context to understand potential motivations of malicious activity.
IAM & Detection Engineering
Discover the importance of IAM event detection and why it's vital to protecting digital assets from cyber threats.

CALISTO doxxing: Sekoia findings concurs to Reuters’ investigation on FSB-related Andrey Korinets
Discover activities linking Korinets to CALISTO doxxing in our investigation. Uncover details from emails, domains & servers used to target UK Parliament & Cambridge University.
ActiveMQ CVE-2023-46604 exploited by Kinsing: Threat analysis
Discover a technical analysis of the exploitation of the CVE-2023-46604 vulnerability by Kinsing intrusion set.
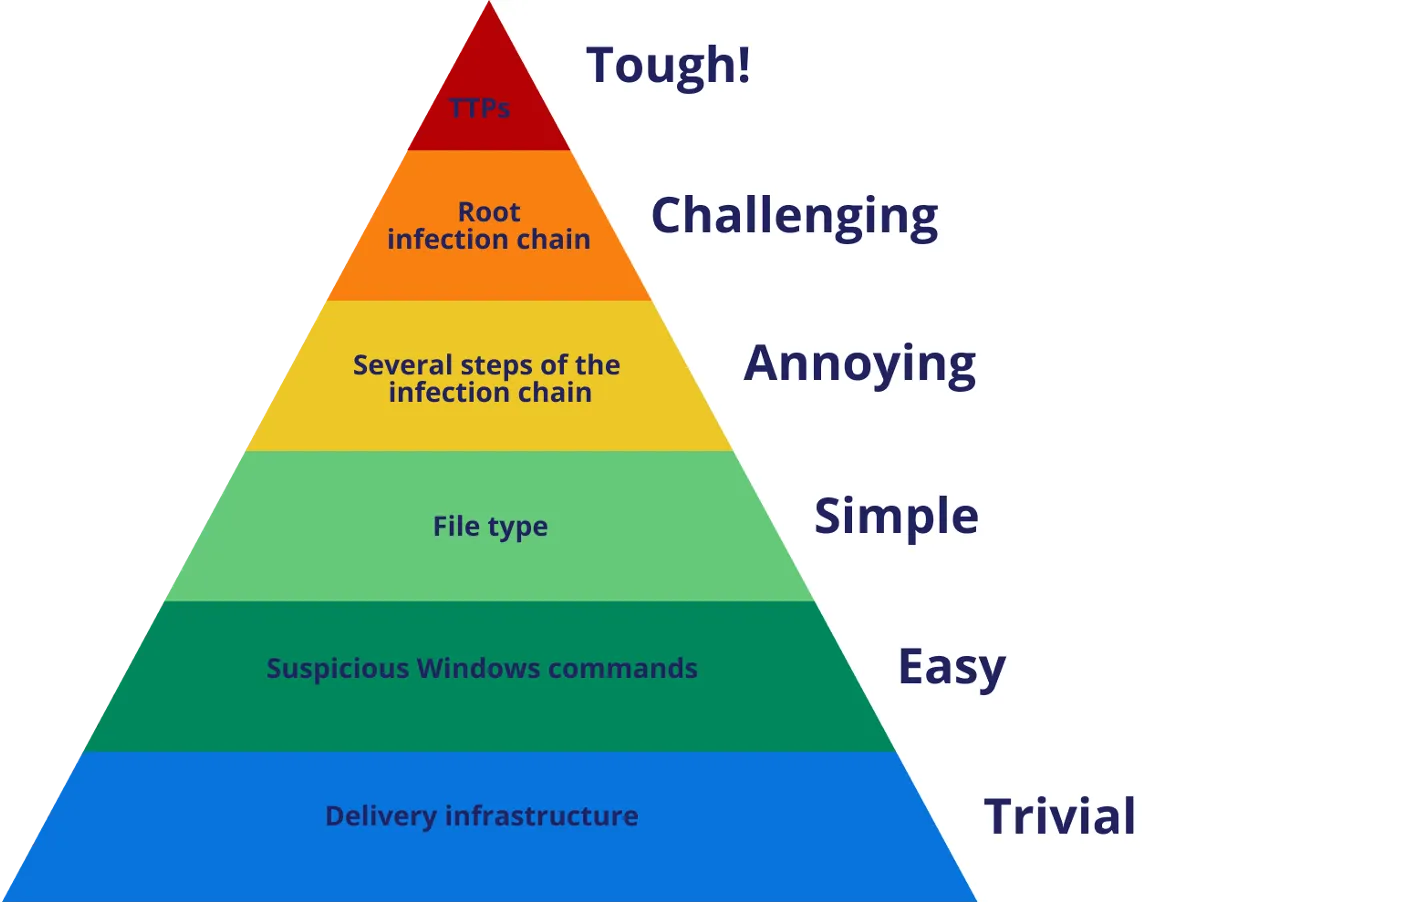
When a botnet cries: Detecting botnet infection chains
Infection chains used by commodity malware are constantly evolving and use various tricks to bypass security measures and/or user awareness. BumbleBee, QNAPWorm, IcedID and Qakbot are all often used as first-stage malicious code.
Unmasking the latest trends of the financial cyber threat landscape
Financial cyber threat analysis: pinpoint common tactics, techniques & procedures used by intrusion sets to protect the financial system.
DarkGate Internals
Learn how DarkGate, a malware-as-service developed in Delphi & C++, is used by threat actors for covert operations & to evade detection.

Game over: Gaming community at risk with information stealers
This report delves into the gaming industry targeted by infostealer malware, and details a specific campaign spreading via Discord messages.

AridViper, an intrusion set allegedly associated with Hamas
Given the recent events involving the Palestinian politico-military organisation Hamas which conducted on 7 October 2023 a military and terrorist operation in Israel, Sekoia.io took a deeper look into AridViper, an intrusion set suspected to be assoc