
Predators for Hire: A Global Overview of Commercial Surveillance Vendors
This report provides an overview of the commercial surveillance vendors ecosystem between 2010 and 2025, analysing their spyware offerings, business models, client base, target profiles, and infection chains.


Bulbature, beneath the waves of GobRAT
Since mid 2023, Sekoia Threat Detection & Research team (TDR) investigated an infrastructure which controls compromised edge devices transformed into Operational Relay Boxes used to launch offensive cyber attack.
SilentSelfie: Uncovering a major watering hole campaign against Kurdish websites
Our investigation uncovered 25 kurdish websites compromised by four different variants of a malicious script, ranging from the simplest, which obtains the device's location, to the most complex, which prompts selected users to install a malicious And


The Predator spyware ecosystem is not dead: Intellexa's active C2 infrastructure and targeted countries
Discover our TDR team's revelations about Predator spyware: its C2 infrastructure and list of countries still using its cyber espionage tool.
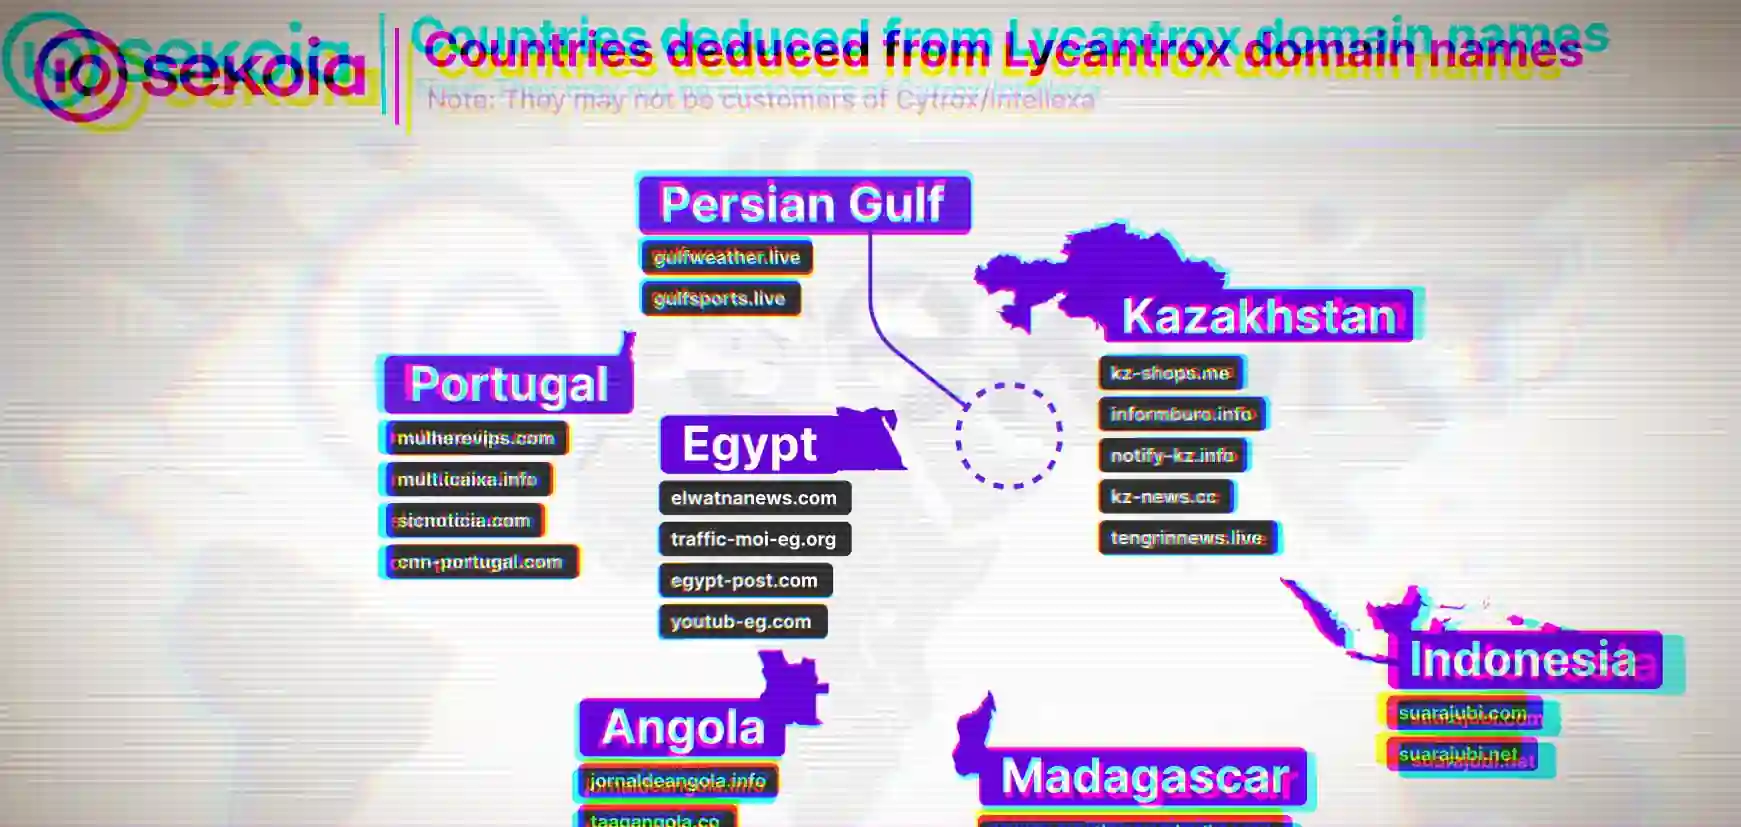
Active Lycantrox infrastructure illumination
Sekoia.io is actively monitoring hundreds of malicious infrastructure clusters to protect its customers. In light of the recent Citizenlab blogspot and in solidarity with the efforts against cyber mercenaries, we have chosen to shed light on one of t