

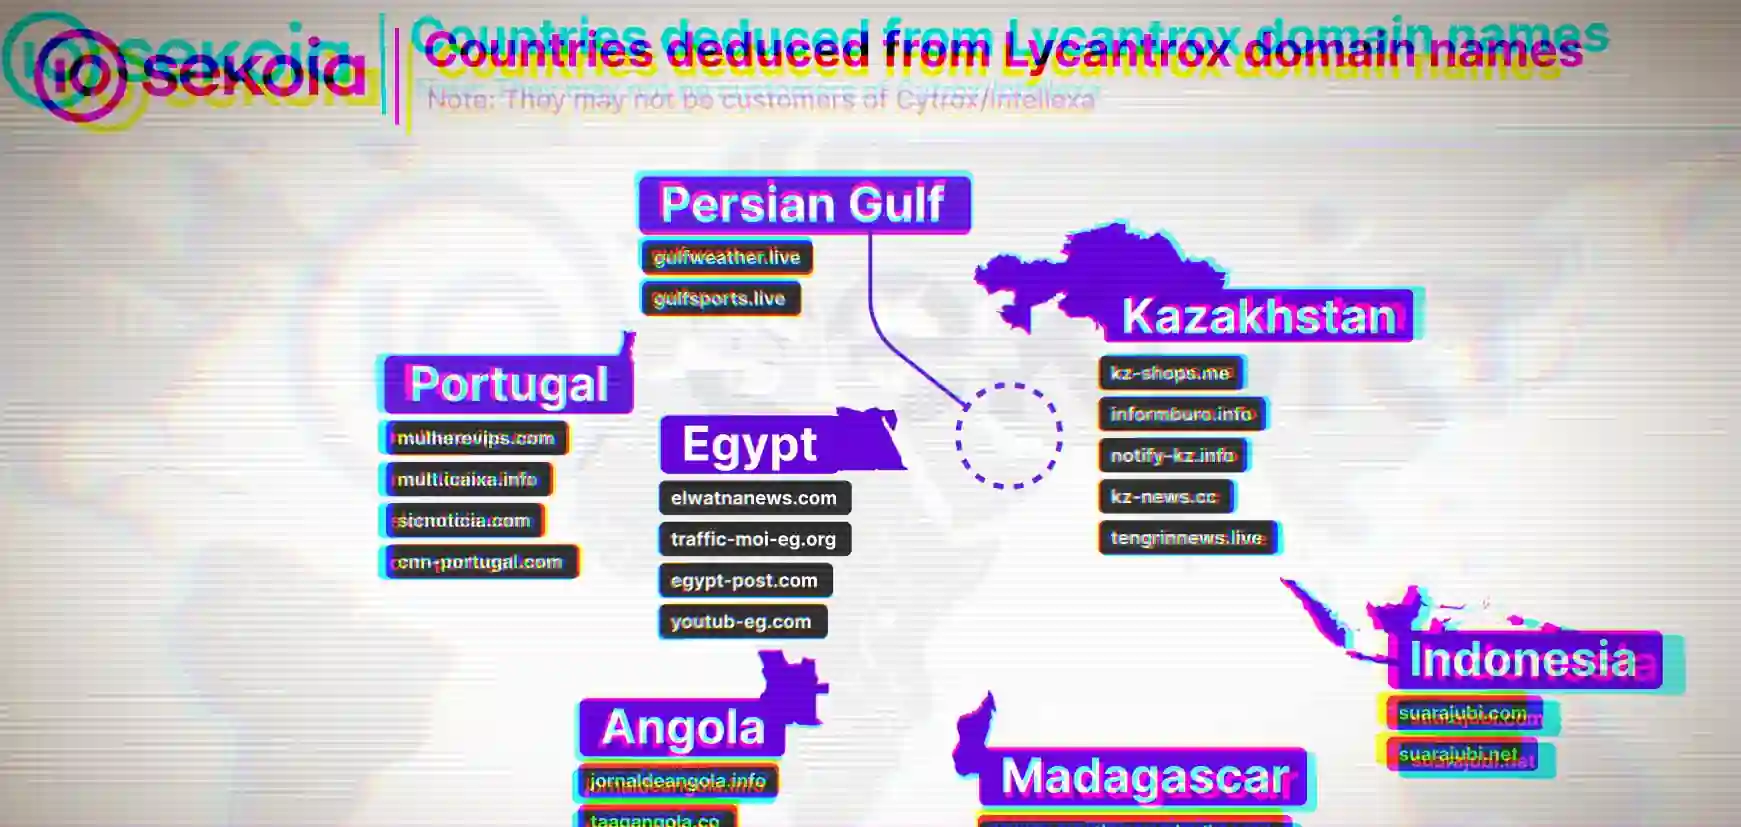
Active Lycantrox infrastructure illumination
Sekoia.io is actively monitoring hundreds of malicious infrastructure clusters to protect its customers. In light of the recent Citizenlab blogspot and in solidarity with the efforts against cyber mercenaries, we have chosen to shed light on one of t

APT28 leverages multiple phishing techniques to target Ukrainian civil society
The APT28 intrusion set (aka. Sofacy, PawnStorm, Fancy Bear), associated to the Russian GRU was observed using multiple phishing techniques to target the Ukrainian civil society.

Sekoia analysis of the #VulkanFiles leak
In January 2023, French newspaper Le Monde offered Sekoia to cooperate on investigating exfiltrated Russian-written documents related to the Moscow-based private company Vulkan.
Peeking at Reaper’s surveillance operations
In this blogpost you will find the results of a survey conducted by our analysts on two Command and Control servers (C2s) of the North Korea-nexus intrusion set Reaper (aka APT37). This investigation led to the uncovering of several phishing webpages

Raspberry Robin's botnet second life
As many botnets and worms, Sekoia analysts demonstrate through this article that Raspberry Robin can be repurposed by other threat actors to deploy their own implants.
Calisto shows interest in entities involved in Ukraine war support
Calisto (aka Callisto, COLDRIVER) is suspected to be a Russian-nexus intrusion set active since at least April 2017. Although it was not publicly attributed to any Russian intelligence service, past Calisto operations showed objectives and victimology that were closely aligned with Russian strategic interests.
LuckyMouse uses a backdoored Electron app to target MacOS
LuckyMouse uses a backdoored Electron app to target MacOS. This is the first time that Sekoia observed LuckyMouse targeting MacOS.
CALISTO continues its credential harvesting campaign
March 30, 2022, Google TAG published several IOCs related to CALISTO, a Russia-nexus threat actor. Discover our analysis.

MSDT abused to achieve RCE on Microsoft Office
Discover through our article, how attackers hijack the Microsoft Support Diagnostic Tool to remotely execute arbitrary code under Windows.

NOBELIUM’s EnvyScout infection chain goes in the registry, targeting embassies
NOBELIUM is another name for the APT29 intrusion set, operated by a threat actor allegedly linked to the SVR.

Log4Shell: The defender’s worst nightmare?
In this blog post, our Threat Detection & Research team answers your questions on Log4Shell.

Walking on APT31 infrastructure footprints
APT31 is an Advanced Persistent Threat group whose mission is likely to gather intelligence on behalf of the Chinese government.