
SentinelOne and Sekoia Integration
Sekoia SOC integrates with SentinelOne EDR for robust cybersecurity. Explore threat event detection, playbooks, and automated actions.
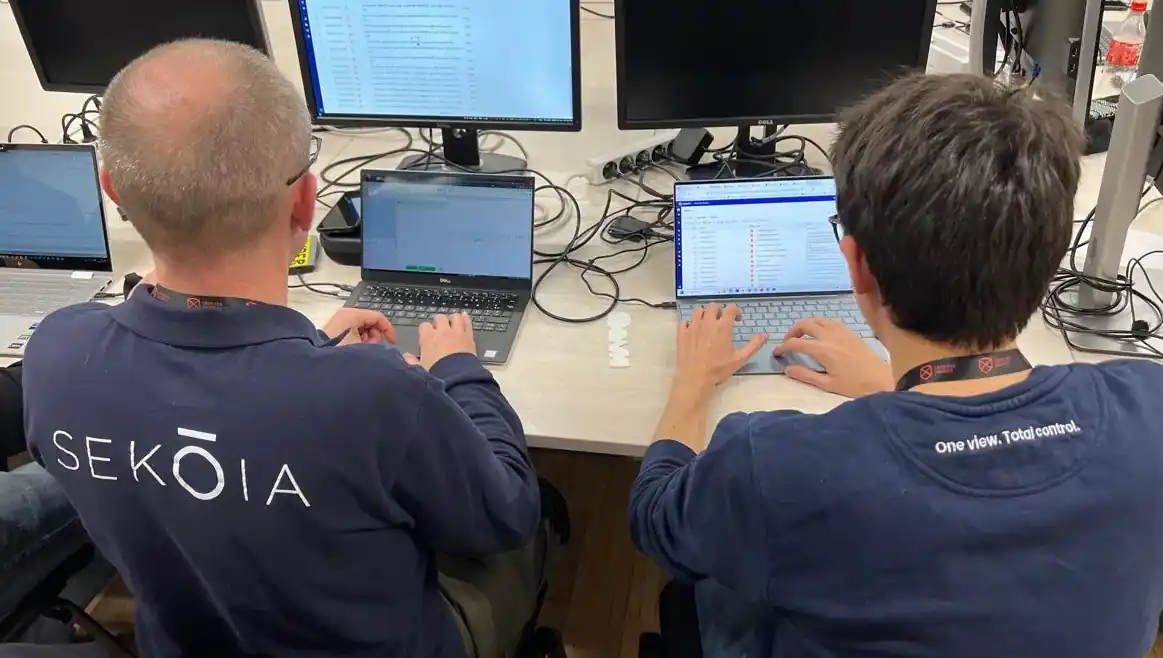
Detecting Berylian attacks: Sekoia SOC Platform used in NATO CCDOE Crossed Swords 2023
Sekoia took part to NATO Cooperative Cyber Defence Centre of Excellence (CCDOE) Crossed Swords cyber exercise organized in Tallinn, Estonia.
Being PCI DSS certified
Being PCI certified is a long journey. We started two years ago when we were discussing an extension of our coverage with a customer. This customer was processing card data and consequently had to be partnering with PCI-compliant security solutions t
How Sekoia empowers cybersecurity with 300+ integrations
Sekoia offers 300+ security integrations - Cloud and SaaS, Endpoints, Network, IAM, Threat Intelligence. Explore our integration roadmap.
Sekoia achieves PCI-DSS compliance
Sekoia is proud to announce that it has achieved the Payment Card Industry Data Security Standard (PCI-DSS) compliance at Level 1.
Revolutionize your security strategy: Introducing automatic asset discovery
In the rapidly evolving cybersecurity landscape, staying ahead of potential threats requires a robust and comprehensive approach to managing IT assets. We are pleased to announce the beta release of our newest feature, Asset Discovery,…
Unveiling the power of the new Query Builder in the Sekoia SOC platform
Discover how the Query Builder simplifies data exploration and enhances your threat detection capabilities with an intuitive interface in Sekoia SOC Platform.
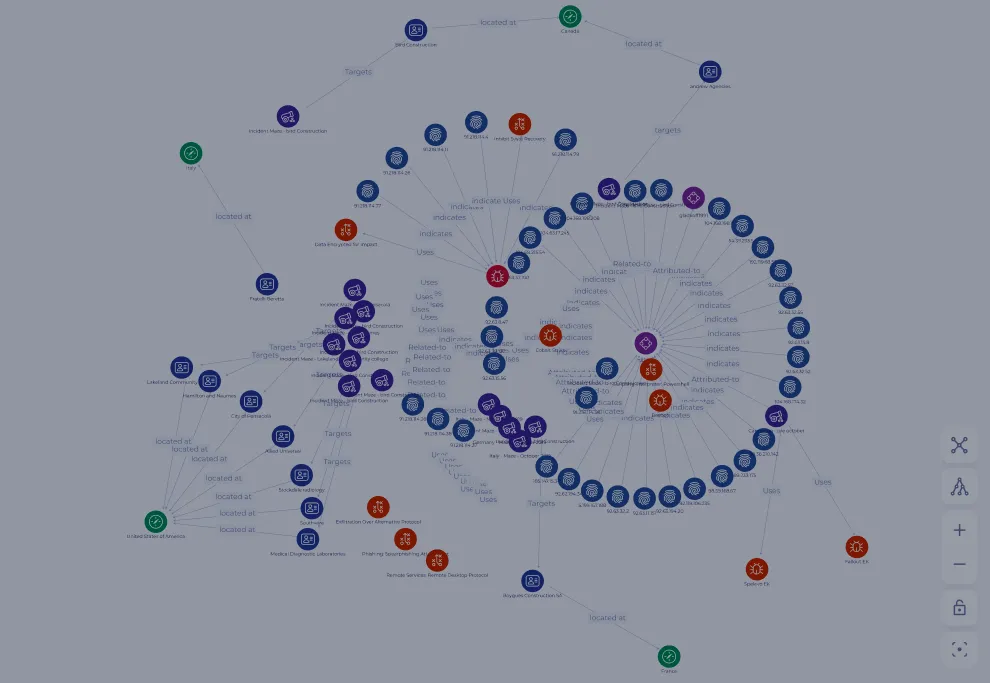
Sekoia CTI at a glance
The CTI produced within Sekoia provides a comprehensive vision on the global cyber-threats alongside technical indicators of compromise (IOC), revealing the presence of attackers. We are in a “one-to-many” model where we are building global intell

Streamline your access with Sekoia's new Single Sign-On (SSO) feature
Sekoia is excited to announce that its Single Sign-On (SSO) feature is now available to all users as a public beta, bringing a host of benefits to streamline your access process.

How to improve data collection from endpoints? (Tutorial 2023)
The SEKOIA.IO Agent is out of Beta. To install it, simply follow the different configuration steps that we detail in this blog post.

How to use Sekoia indicators in Microsoft Sentinel ?
Sekoia.io indicators can be integrated into Microsoft Sentinel One. In this blogpost, discover how to take advantage of this integration.
Threat intelligence is not (only) on a spectrum
Cyber Threat Intelligence can vary widely, between raw streaming of observables up to fully contextualised curation of bespoke threat models