Sekoia Self-Hosted
Modern security operations inside your own perimeter
Deploy Sekoia in customer-selected infrastructure, including private cloud, on-premises, restricted, and air-gapped environments.
Get a demo
Bring modern security operations home
The full platform, on your infrastructure
Support the requirements of government, defense, critical infrastructure, and regulated organizations operating under strict sovereignty, connectivity, or procurement constraints.
One platform, not a patchwork
Bring detection, investigation, threat intelligence, response, automation, and agentic workflows into one connected security operations platform.
Updates on your schedule
Use signed artifacts, structured releases, deployment tooling, operational runbooks, and predictable content updates to support the operational requirements of self-hosted environments.
Keep modern capabilities
Self-Hosted is a deployment model, not a reduced version of Sekoia. Extend modern security operations into environments where SaaS is not viable, with capabilities and module availability managed transparently by release.
When SaaS is not an option
Your data stays in your perimeter
Sovereignty, classification and regulations such as NIS2 and DORA can require security data to stay on infrastructure you control.
Restricted networks limit connectivity
Disconnected, isolated, or air-gapped environments cannot rely on continuous access to public-cloud services and external platforms.
Fragmented tools create operational gaps
On-premises security tools often provide incomplete visibility, while disconnected products make it harder to connect detection, investigation, intelligence, and response.
Manual work slows the SOC down
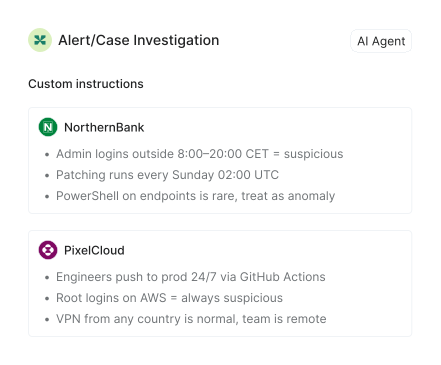
Detection content can become outdated, investigations remain largely manual, and analysts spend too much time triaging noise instead of focusing on the decisions that matter.
Multiply your team’s capacity
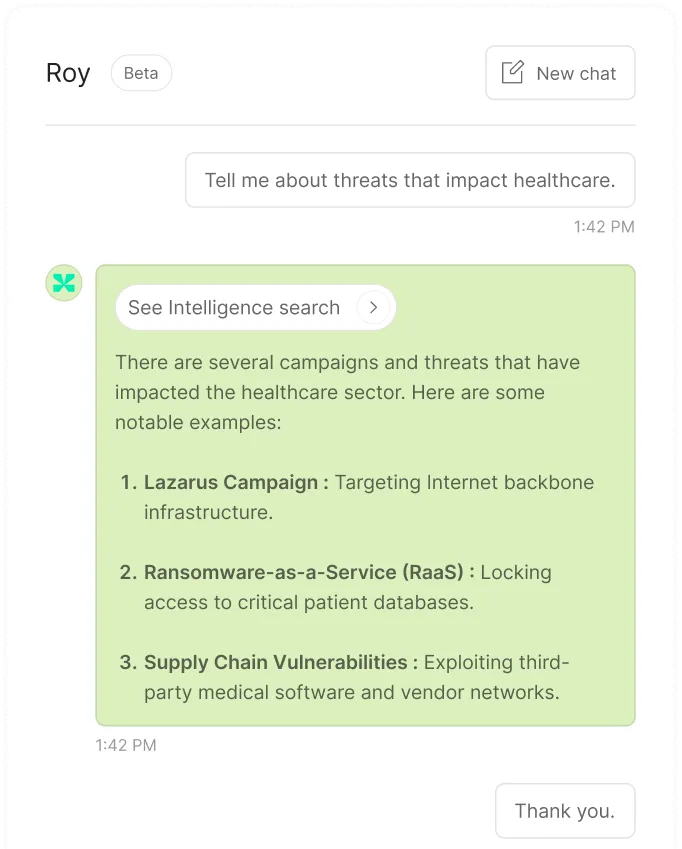
Sekoia Self-Hosted gives security teams a predictable way to run a modern SOC where SaaS cannot go. Agentic AI can help correlate signals, connect relevant context, and support repetitive investigation work. Your teams define where automation applies, what gets escalated, and when human approval is required.
Reduce repetitive analyst work
Automate recurring analysis and investigation tasks so analysts can spend more time on complex decisions and high-value security work.
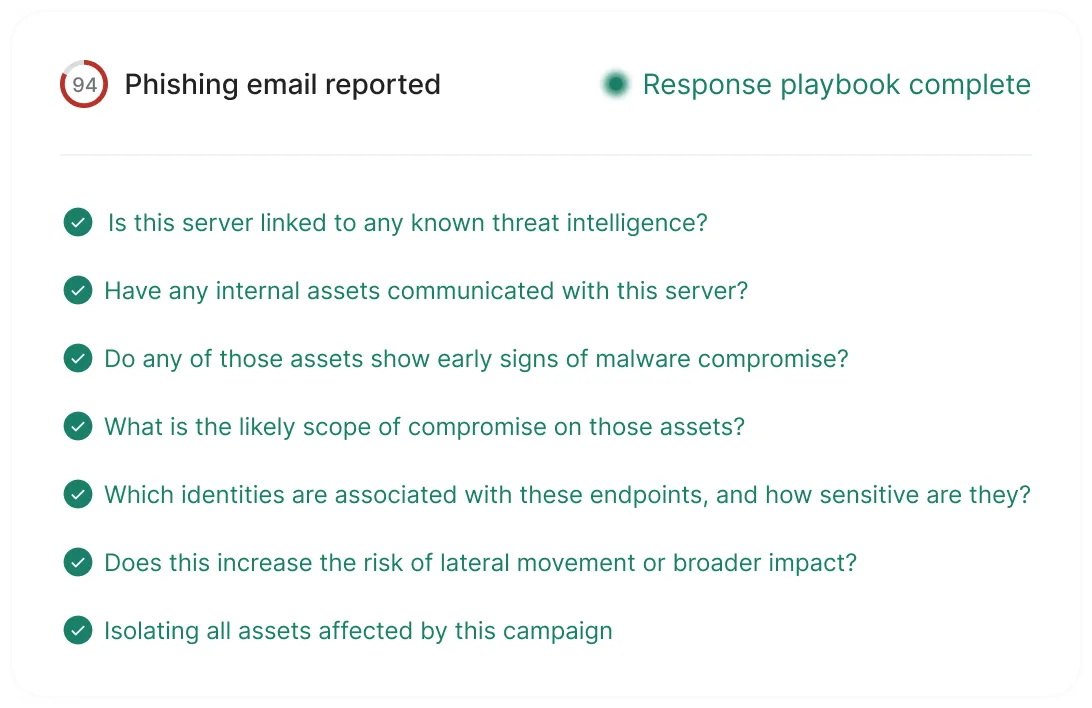
Accelerate investigation
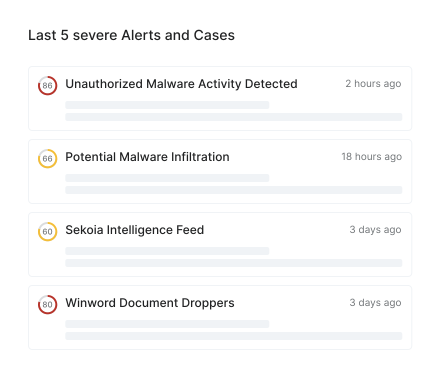
Connect events, entities, detections, and threat intelligence to build context faster and move from alert to understanding with less manual effort.
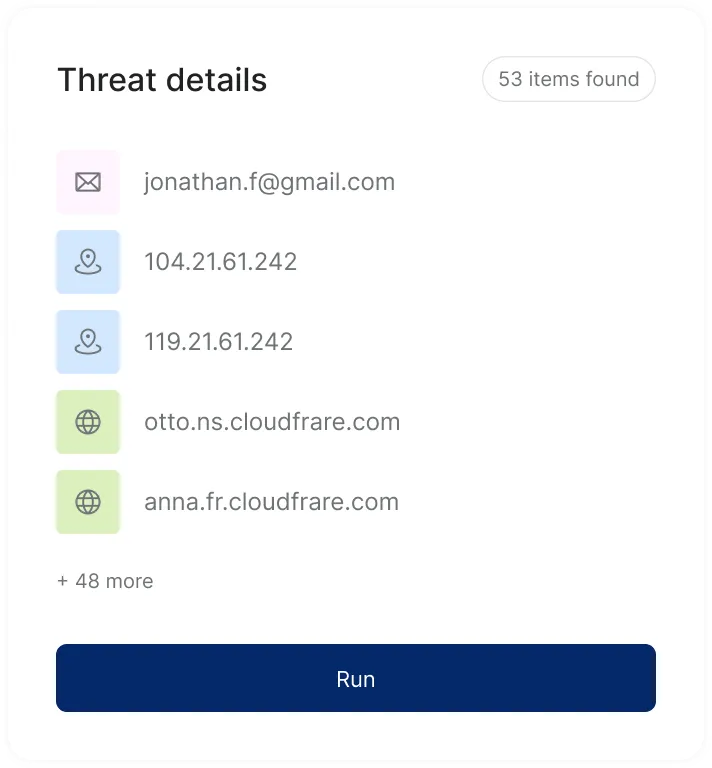
Respond with greater consistency
Support response workflows with guided actions, automation, and clearly defined human approval points.
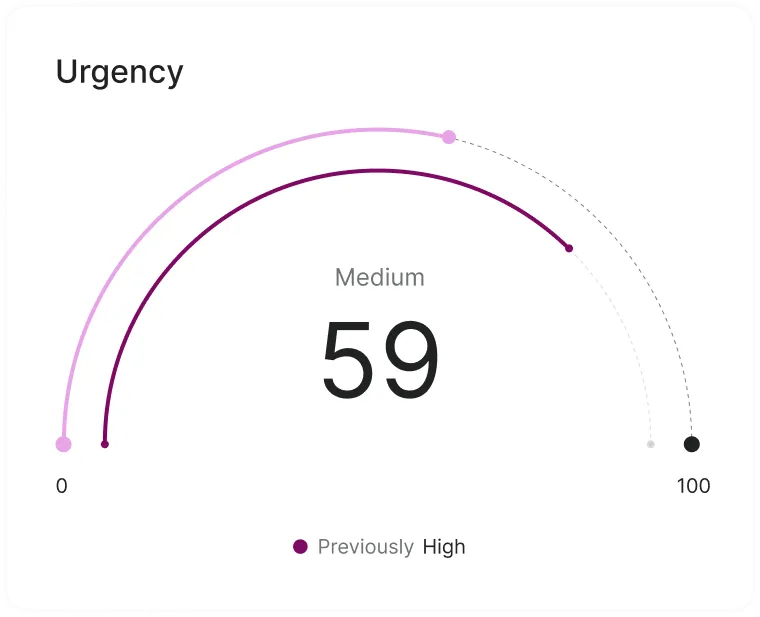
Operate with greater predictability
Use a structured approach to deployment, upgrades, monitoring, support, and lifecycle management across restricted and customer-controlled environments.
Talk to a deployment expert
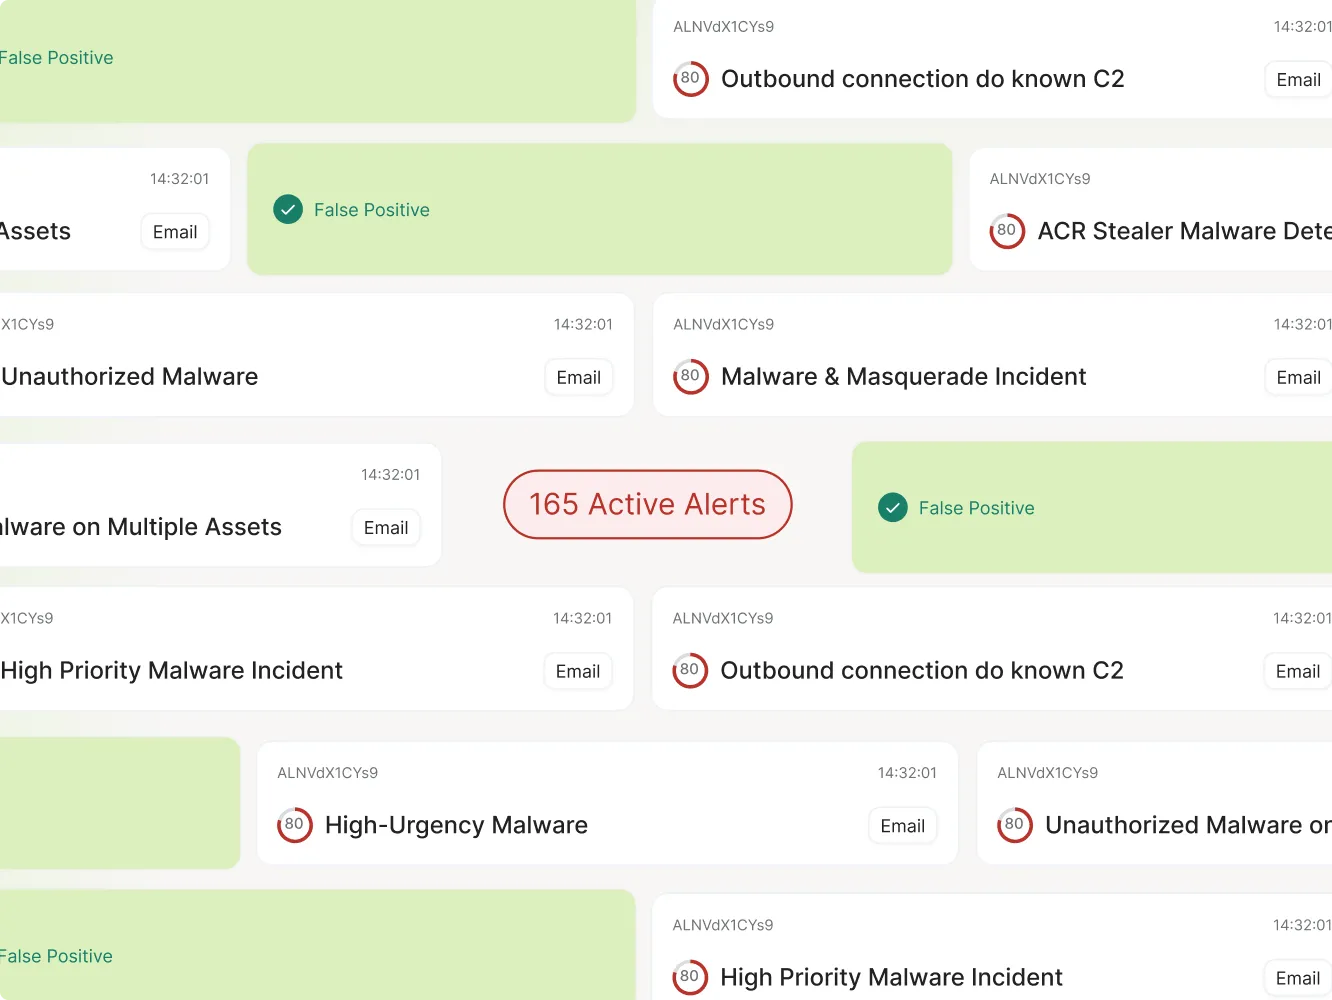
Unite your defense
From detection to investigation and response, Sekoia connects your SOC team, intelligence, and workflows so you can act faster. And with greater clarity and confidence.
Identify threats across your environment with detection enriched by threat intelligence, behavioral analysis, and agentic reasoning.
Agentic Workflows
Unified Intelligence
Adaptive Detection Models
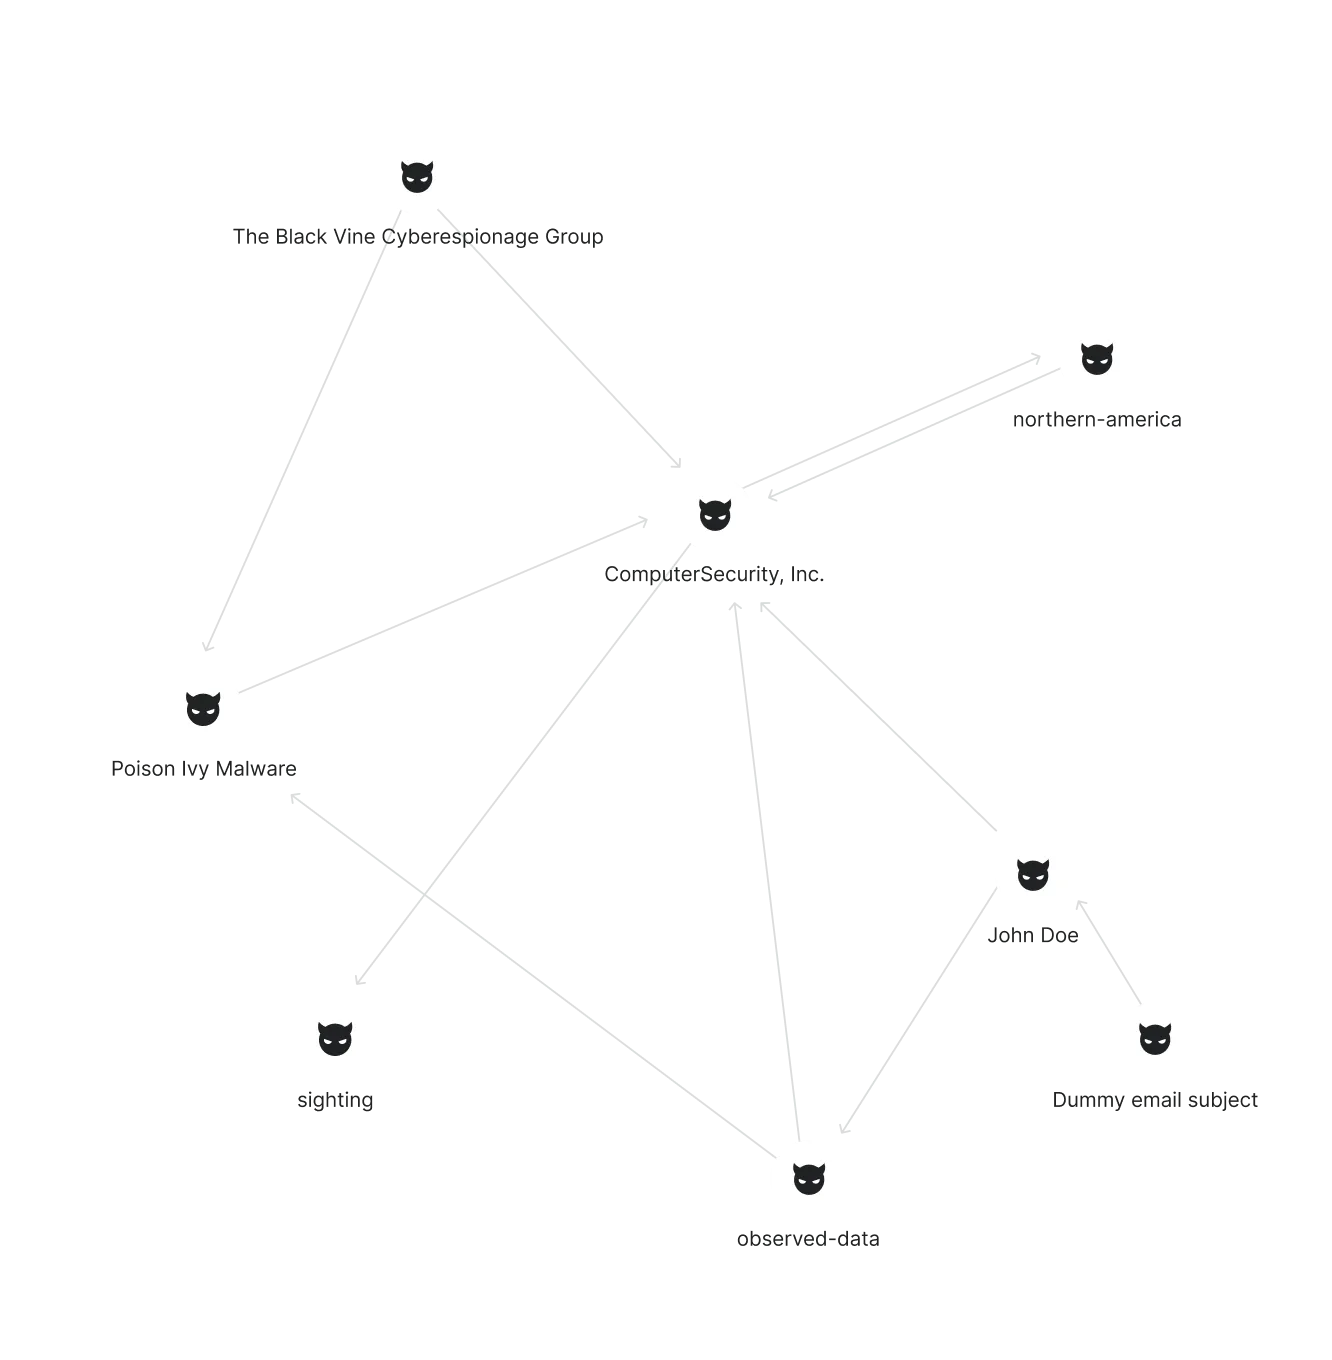
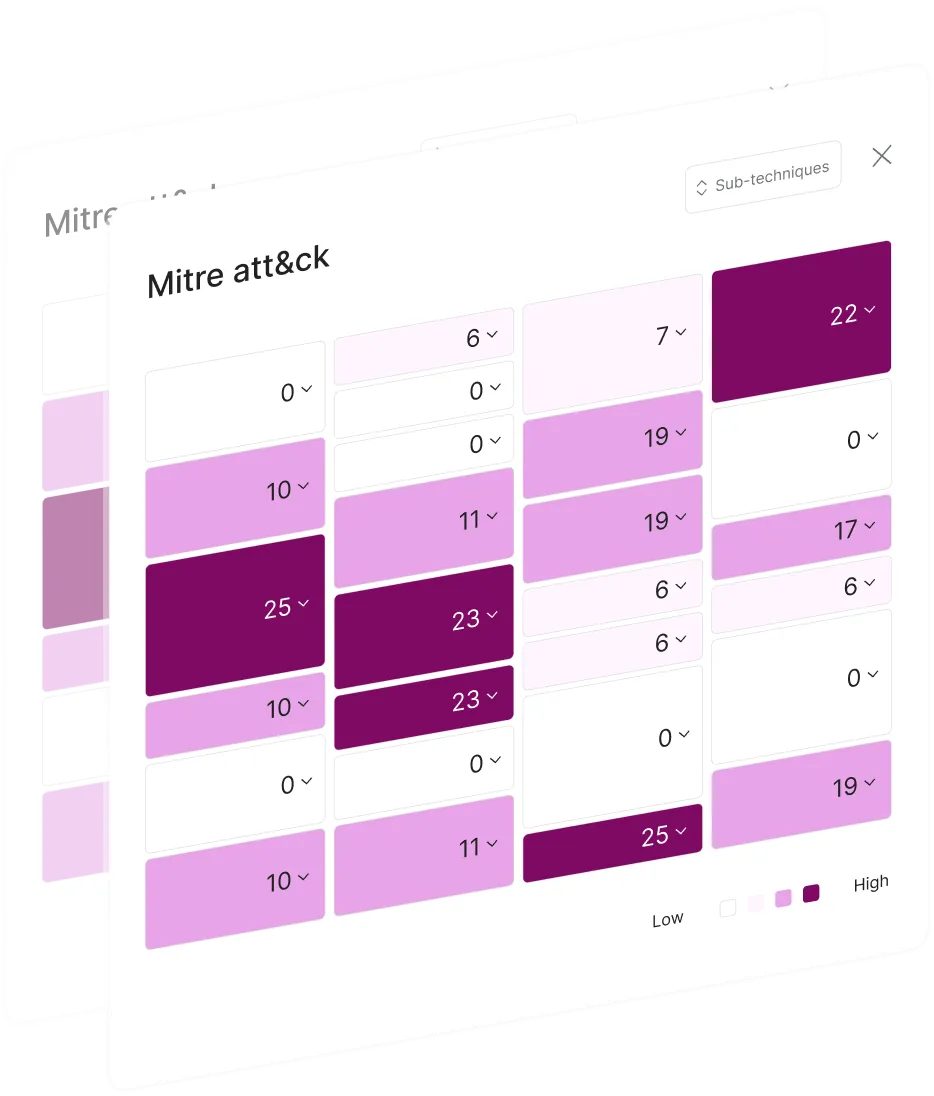

Automate repetitive analysis and connect events, entities, alerts, and intelligence to build investigation context faster.
Intelligence Led Threat Hunting
Fully Guided Hunts
Continuous Adversary Tracking
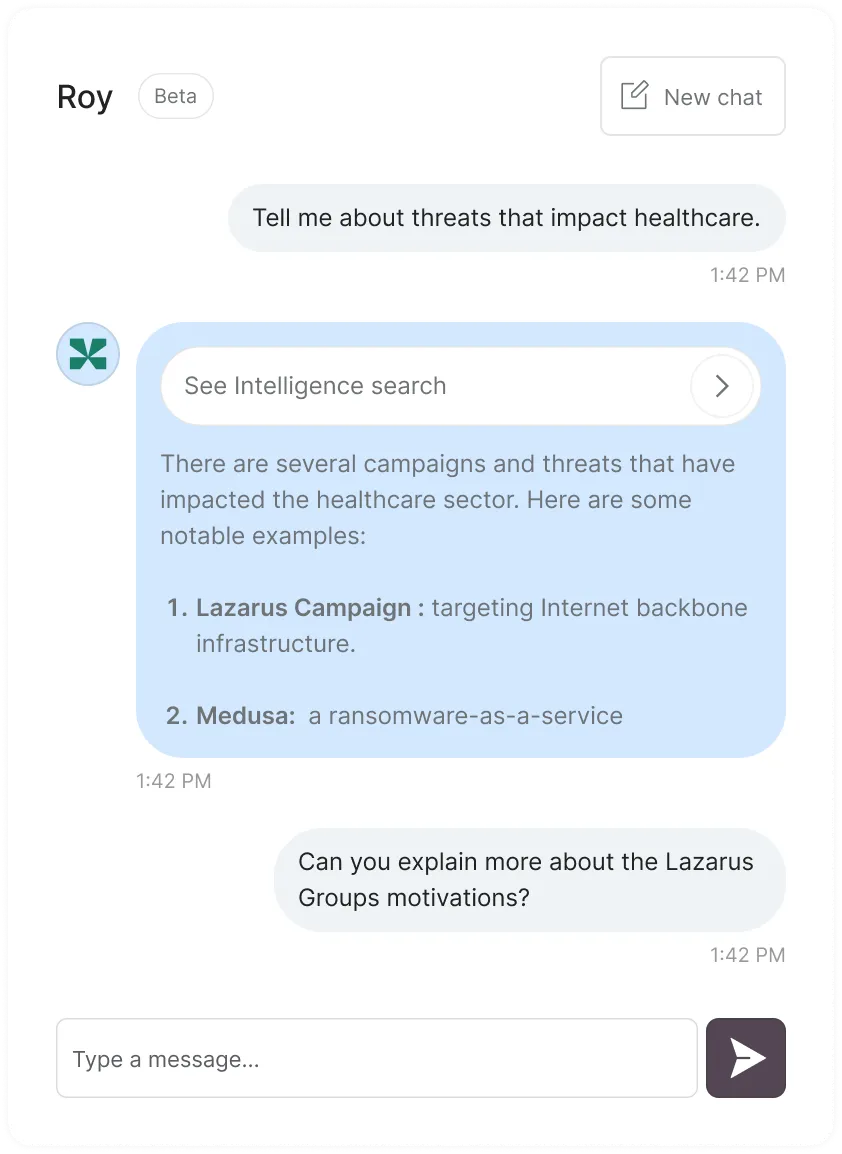
Bring detection, investigation, and threat intelligence together in one operational view, helping analysts move from noise to informed decisions.
Automated Evidence Gathering
Ask-Anything Analysis
Completely transparent
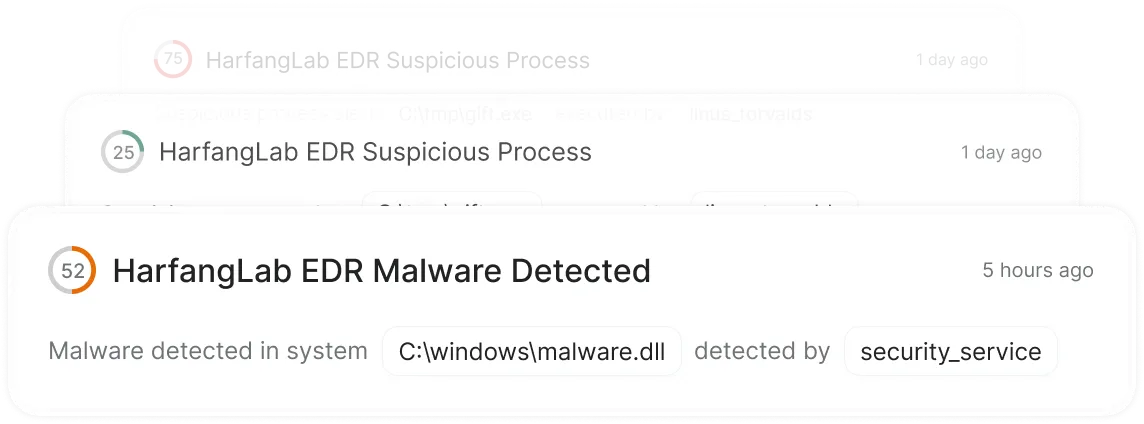
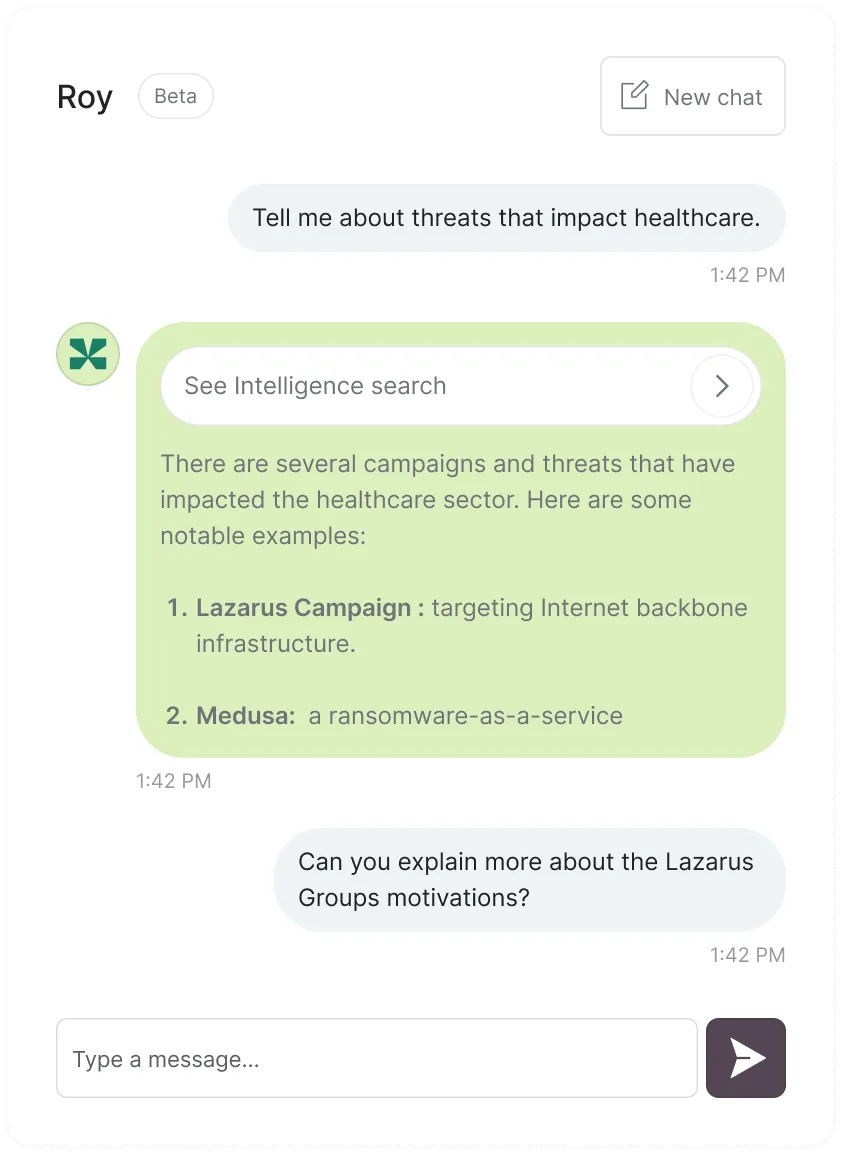
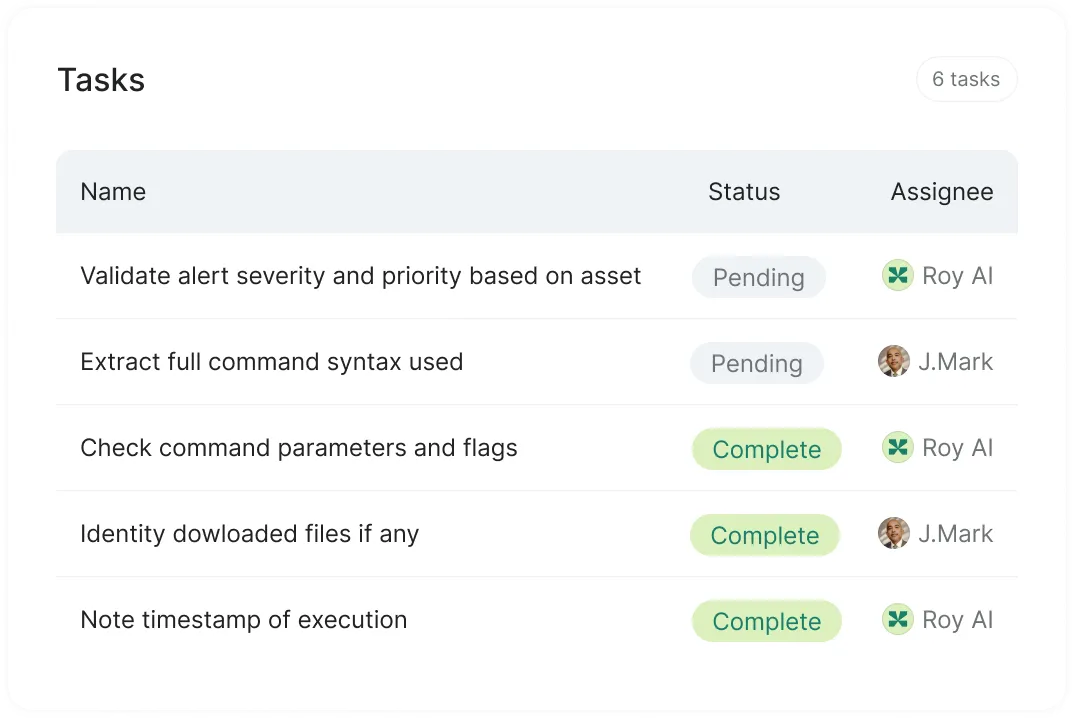
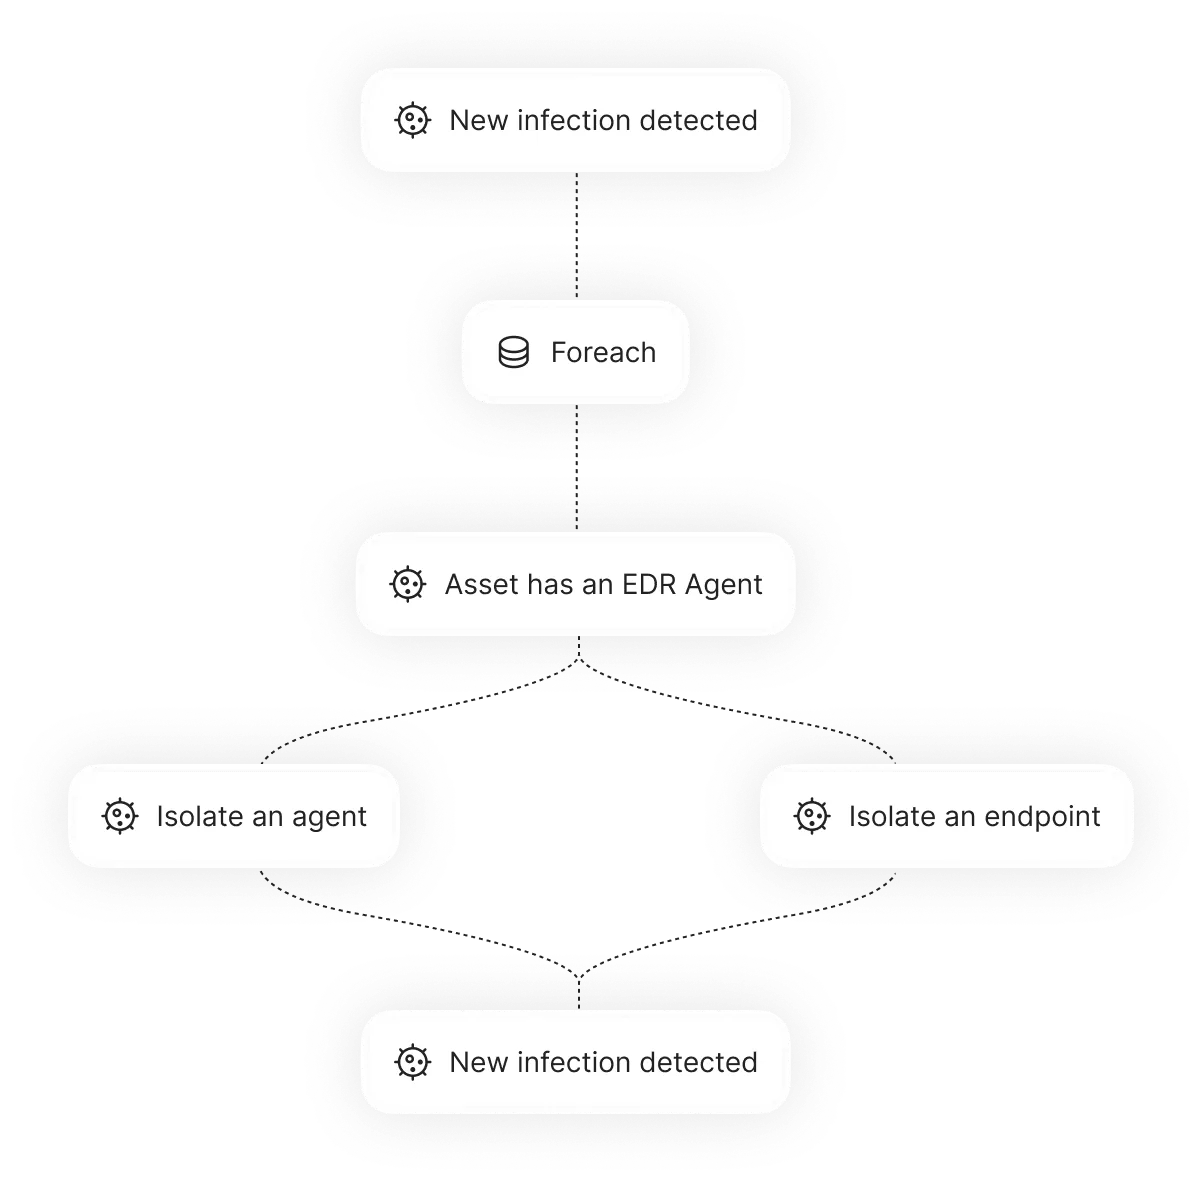
Accelerate triage with guided actions, workflow automation, and clearly defined human approval points.
Playbooks that Evolve
Orchestrated Enterprise-Wide Response
Autonomous Containment
Designed for organizations where SaaS is not an option
● Restricted or disconnected networks
● Classified or sensitive environments
● Regulatory and procurement constraints
● Customer-controlled infrastructure
● Local operation by internal teams or a trusted MSSP
Keep your data and infrastructure under control while giving analysts the intelligence, automation, and agentic capabilities they need to work faster and respond with confidence.
Get a demo