

Calisto shows interest in entities involved in Ukraine war support
Calisto (aka Callisto, COLDRIVER) is suspected to be a Russian-nexus intrusion set active since at least April 2017. Although it was not publicly attributed to any Russian intelligence service, past Calisto operations showed objectives and victimology that were closely aligned with Russian strategic interests.
Lucky Mouse: Incident Response to Detection Engineering
This blogpost discusses how the Tactics, Techniques and Procedures (TTPs) used by the APT27 (Lucky Mouse) intrusion set in the last incident reported by Intrinsec, a Sekoia Managed Security Service Provider (MSSP) partner, are detected using SEKOI

Aurora: A rising stealer flying under the radar
Sekoia analysed Aurora in depth and share the results of our investigation in this article.
BlueFox Stealer: A newcomer designed for traffers teams
In September 2022 during routine Dark Web monitoring we identified BlueFox Stealer v2, a newly-advertized information stealer sold as MaaS.

XDR detection engineering at scale: Crafting detection rules for SecOps efficiency
In this blog post we present Sekoia’s process to create detection rules, which first requires explaining our detection workflow as well as understanding Sekoia XDR history and specificities.
PrivateLoader: The loader of the prevalent ruzki PPI service
Sekoia analysts tracked PrivateLoader’s network infrastructure for several months and recently conducted an in-depth analysis of the malware. In parallel, we also monitored activities related to the ruzki PPI malware service.
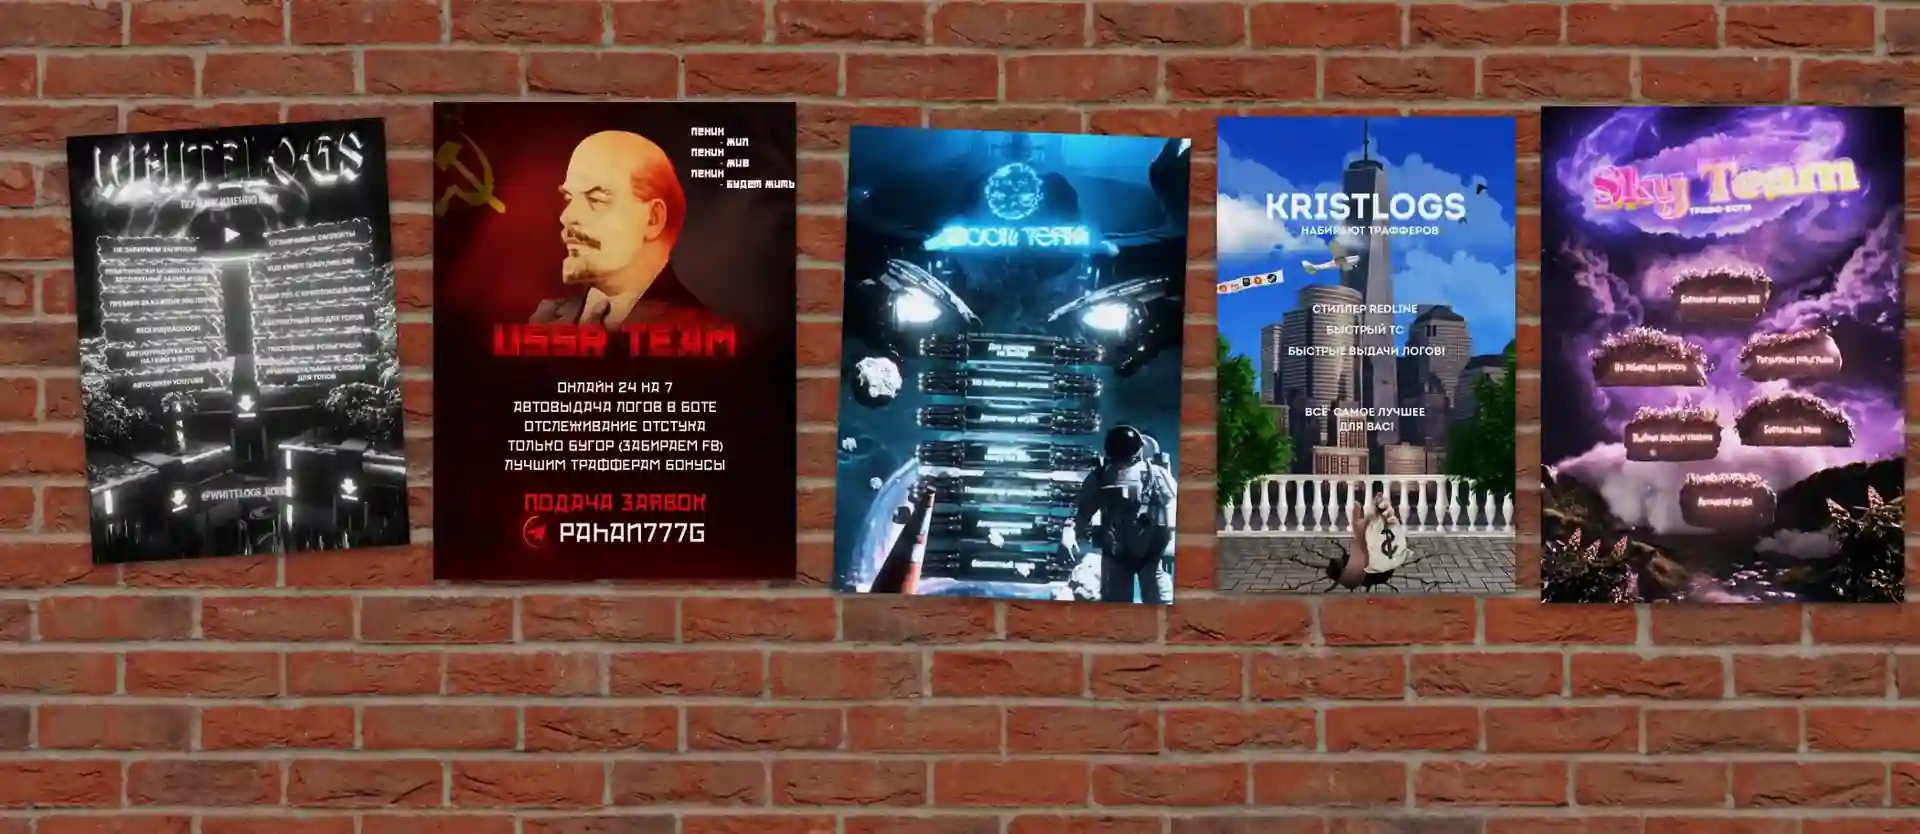
Traffers: A deep dive into the information stealer ecosystem
Traffers are responsible for redirecting user traffic to malicious content (malware, fraud, phishing, scam) exploited by other threat actors.
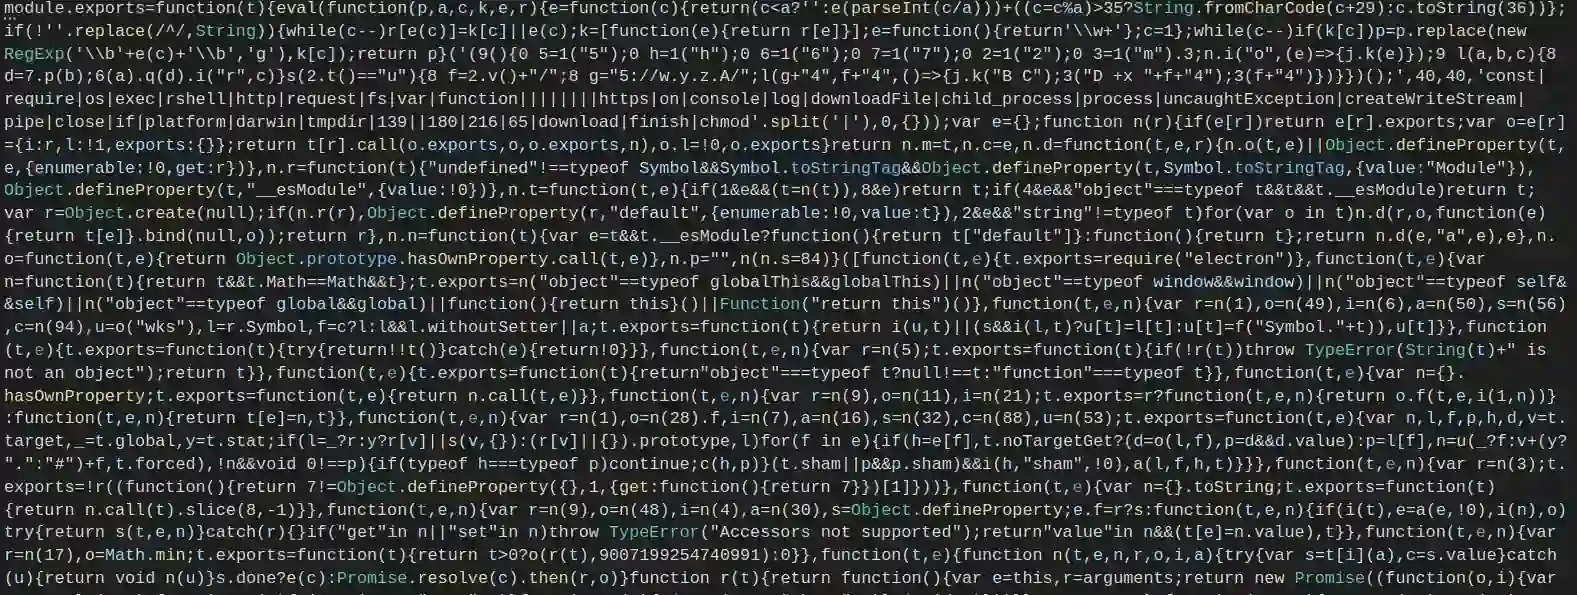
LuckyMouse uses a backdoored Electron app to target MacOS
LuckyMouse uses a backdoored Electron app to target MacOS. This is the first time that Sekoia observed LuckyMouse targeting MacOS.

Sekoia mid-2022 ransomware threat landscape
Sekoia presents its Ransomware threat landscape for the first semester of 2022, with the following key points...
Ongoing Roaming Mantis smishing campaign targeting France
MoqHao (aka Wroba) is an Android Remote Access Trojan (RAT) with information-stealing and backdoor capabilities that likely spreads via SMS.
Vice Society: A discreet but steady double extortion ransomware group
Vice Society is a little-known double extortion group that exfiltrates its victims' data and threatens its victims to leak their information.
Raccoon Stealer v2 - Part 2: In-depth analysis
This blog post is a technical analysis of the new Raccoon Stealer 2.0 stand-alone version. Authors have announced that the malware is also available in a DLL format or could be embedded in other PE.