


Russian-speaking infostealer ecosystem: The distribution
This blog post aims at presenting the main techniques, tools and social engineering schemes used by the cybercriminals from the Russian-speaking infostealer ecosystem and observed by Sekoia analysts in the past year.
The energy sector 2022 cyber threat landscape
This report is a joint CITALID and SEKOIA analysis pertaining to cyber activities targeting the energy sector in 2022 in Europe. It is based on open sources reports and includes both our investigations and analysis. Information cut-off date is 22

Sekoia analysis of the #VulkanFiles leak
In January 2023, French newspaper Le Monde offered Sekoia to cooperate on investigating exfiltrated Russian-written documents related to the Moscow-based private company Vulkan.
Stealc: A copycat of Vidar and Raccoon infostealers gaining in popularity - Part 2
This blog post is a technical analysis of Stealc infostealer, detailing different characteristics of the malware, including anti analysis, strings de-obfuscation and C2 communication techniques.
One year after: The cyber implications of the Russo-Ukrainian war
One year after the start of Russo-Ukrainian War, our analysts share through their analysis pertaining to the cyber picture.

Stealc: a copycat of Vidar and Raccoon infostealers gaining in popularity - Part 1
This blogpost aims at presenting the activities of the Stealc’s alleged developer, a technical analysis of the malware and its C2 communications, and how to track it.

Sekoia Ransomware Threat Landscape (second-half 2022)
This blog post aims at analysing and highlighting trends within the ransomware ecosystem in the second half of 2022

Command & Control infrastructures tracked by Sekoia in 2022
Throughout 2022, Sekoia's Threat & Detection Research (TDR) team continued to proactively track and monitor the Command & Control (C2) infrastructures set up and used by cybercriminal or state sponsored intrusion sets to carry out malicious cyber

Raspberry Robin's botnet second life
As many botnets and worms, Sekoia analysts demonstrate through this article that Raspberry Robin can be repurposed by other threat actors to deploy their own implants.

Unveiling of a large resilient infrastructure distributing information stealers
This blogpost aims at presenting the current infection chain, payloads and the whole infrastructure used to distribute infostealers
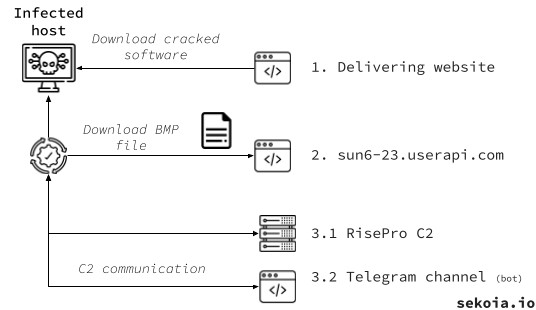
New RisePro Stealer distributed by the prominent PrivateLoader
This article aims at presenting Sekoia's RisePro information stealer analysis.
The DPRK delicate sound of cyber
Discover malicious activities associated to the DPRK-nexus Intrusion Sets (Kimsuky and Lazarus group) reported in open sources in 2022.