Imagine taking the full power of a cloud-grade SOC and placing it safely under a dome. Inside, everything runs at machine speed, including threat detection, automated triage, and deep analytics. Outside, the public internet continues its chaos, but not a single piece of your data ever leaves that perimeter.That is the exact balance highly regulated sectors are looking for today.
A different set of rules for critical sectors
Cloud-native SaaS is the go-to for modern security operations. It's fast, agile, and how most organizations stay ahead of threats without worrying about infrastructure upkeep. At Sekoia, that's still our primary focus.
But we also know that highly regulated sectors and critical infrastructure operate by a different set of rules.
For these teams, a traditional public cloud model creates real challenges:
- The compliance ceiling: Evolving national sovereignty requirements and strict regulations like NIS2 create an immediate roadblock for public-cloud-dependent security tools.
- Network limitations: When you operate in classified or completely restricted networks, external internet connectivity simply isn't an option, no matter how secure a cloud provider claims to be.
- Absolute autonomy: Defense, government, and vital infrastructure entities require total, uncompromising control over their underlying systems.
SaaS hasn't failed. But for critical industries, an architectural evolution is underway, bringing cloud-grade capabilities safely inside your own perimeter.
Why owning your stack is the new standard for highly regulated sectors
Owning your stack (and the data sovereignty that comes with it) is a rising conversation.
- Approximately 70% of all cyberattacks involved critical infrastructure in 2024 alone.
- 22% of critical infrastructure organizations have little or no confidence in identifying where their data is stored.
- 86% of CIOs are planning to move some public cloud workloads back to private cloud or on-premises.
But moving back to your own infrastructure doesn’t mean you’re stuck with legacy tech. Instead, it's a move toward operational maturity. Local deployment gives critical sectors what they actually need: modern, automated detection and response, paired with total control over where your data lives. It’s sovereignty by design. You also gain the ability to run a fully independent Security Operations Center (SOC) with zero external connectivity, isolated from public cloud dependencies entirely.
Introducing Sekoia… self-hosted
Built specifically for high-security environments, Sekoia self-hosted delivers everything you need to run an independent SOC:
- Digitally signed binaries, Docker images, and Helm charts for a verifiable supply chain.
- A dedicated deployment CLI and detailed runbooks to automate your platform lifecycle.
- Weekly threat intelligence and detection rule updates that are fully compatible with air-gapped systems.
We've already onboarded our first users and will be rolling the platform out live over the coming months.
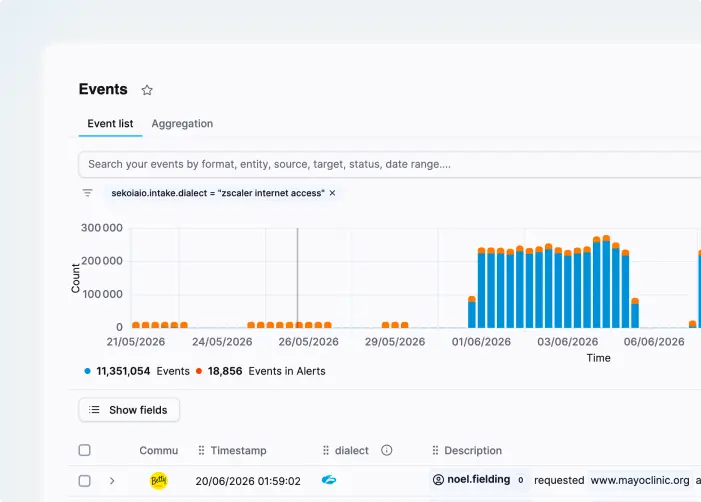
What self-hosted means for critical sector SOC teams
Shifting to a self-hosted model changes the daily operational reality for your team in a few major ways:
- Cloud-grade performance on your terms: You get Sekoia’s core detection, triage, and automation capabilities. Feature parity will scale progressively, with specialized AI agent layer (Elevate) and full CTI capabilities landing across late 2026 and 2027 releases.
- Complete independence: Your team operates entirely autonomously, free from the uptime variables or policy shifts of third-party public cloud providers.
- A predictable lifecycle: No surprise upgrades. Your team controls the deployment, monitoring, and patch cycles through a structured versioning model.
- Resilient by design: High availability isn't an afterthought. The platform is anchored by a 6-node minimum architecture to ensure ingestion and detection keep running seamlessly, even if a node fails.
Self-hosted vs. SaaS deployment models
Here’s a closer look at how the two models differ.
| Sekoia SaaS | Sekoia self-hosted | |
|---|---|---|
| The core AI SOC engine | Fully available Grounded in unified telemetry and AI automation. |
Core detection engine Core capabilities available, with progressive feature parity rollout through late 2026 and 2027. |
| How it's deployed | Managed securely within Sekoia's global cloud infrastructure with zero setup overhead. | Customer-deployed using digitally signed binaries, Docker images, and Helm charts via a dedicated deployment CLI. |
| Who it's for | Organizations of any scale looking for rapid cloud adoption and continuous, automated platform scaling. | Large-scale enterprises, government bodies, and defense entities running dedicated security operations. |
| Compliance and sovereignty | Aligned with standard global enterprise cloud security practices. | Compliant with strict national regulations, sector-specific laws, and national sovereignty frameworks. |
| Network and connectivity | Requires continuous external internet connectivity to access the cloud platform. | Fully compatible with isolated, classified, or 100% air-gapped networks with zero external connectivity. |
| Updates and protection | Continuous, real-time platform upgrades and threat intelligence delivery. | Predictable lifecycle model with structured version updates and weekly secure content drops. |
| Multi-tenancy approach | Native multi-tenant Designed for distributed teams and standard MSSPs to manage multiple accounts from a single cloud interface. |
Sovereign multi-tenant Enables enterprise groups and sovereign service providers to manage multiple entities with strict logical and data isolation. |
| Module availability | All modules available Full, immediate access to Defend, Intelligence, Reveal, and Elevate out of the box. |
Core engine at GA Launches with core Defend features, with additional modules (like Elevate AI and custom apps) rolling out progressively on the roadmap. |
| Scalability | Dynamic Resources can be scaled up or down instantly based on demand, managed entirely by Sekoia without infrastructure constraints. |
Constrained Scaling is capped by your available hardware and requires active provisioning, configuration, and manual resource management. |
| Cost model | OPEX (Operating Expenses) Predictable, ongoing subscription fees that qualify as operational costs; low upfront entry barrier. |
CAPEX (Capital Expenditures) Heavy upfront investments in infrastructure, supplemented by ongoing maintenance overhead. |
A quick honesty check: Is self-hosted right for you?
Because this platform is built for heavy enterprise workloads, it requires serious operational scale. Before diving in, it's worth checking your alignment against our current boundaries:
| The scale requirement | The expertise profile | The current boundaries |
|---|---|---|
| Reserved for large-scale operations protecting a minimum of 5,000 assets or ingesting at least 500GB of data per day. | Requires a dedicated, certified internal team or a trusted MSSP to handle infrastructure ops and lifecycle management. | In our initial General Availability rollout, specialized modules or certain app configurations may have minor variations from our SaaS baseline. |
Let's start a conversation
Every organization faces its own mix of regulations, infrastructure limits, and security goals. If you checked the boxes for a self-hosted architecture, our team is ready to guide you through the mandatory build phase and introduce you to your future Technical Account Manager (TAM).
And if local deployment isn't the right fit? All good! Our core SaaS platform is alive, well, and continuously scaling to protect enterprises globally.
Book a slot to chat through your options with us.