

Sekoia Blogs
DarkGate Internals
Learn how DarkGate, a malware-as-service developed in Delphi & C++, is used by threat actors for covert operations & to evade detection.
Unveiling the power of the new Query Builder in the Sekoia SOC platform
Discover how the Query Builder simplifies data exploration and enhances your threat detection capabilities with an intuitive interface in Sekoia SOC Platform.

Game over: Gaming community at risk with information stealers
This report delves into the gaming industry targeted by infostealer malware, and details a specific campaign spreading via Discord messages.

AridViper, an intrusion set allegedly associated with Hamas
Given the recent events involving the Palestinian politico-military organisation Hamas which conducted on 7 October 2023 a military and terrorist operation in Israel, Sekoia.io took a deeper look into AridViper, an intrusion set suspected to be assoc
ClearFake: A newcomer to the "fake updates" threat landscape
ClearFake is a new malicious JavaScript framework deployed on compromised websites to deliver further malware using the drive-by download technique.
Active Lycantrox infrastructure illumination
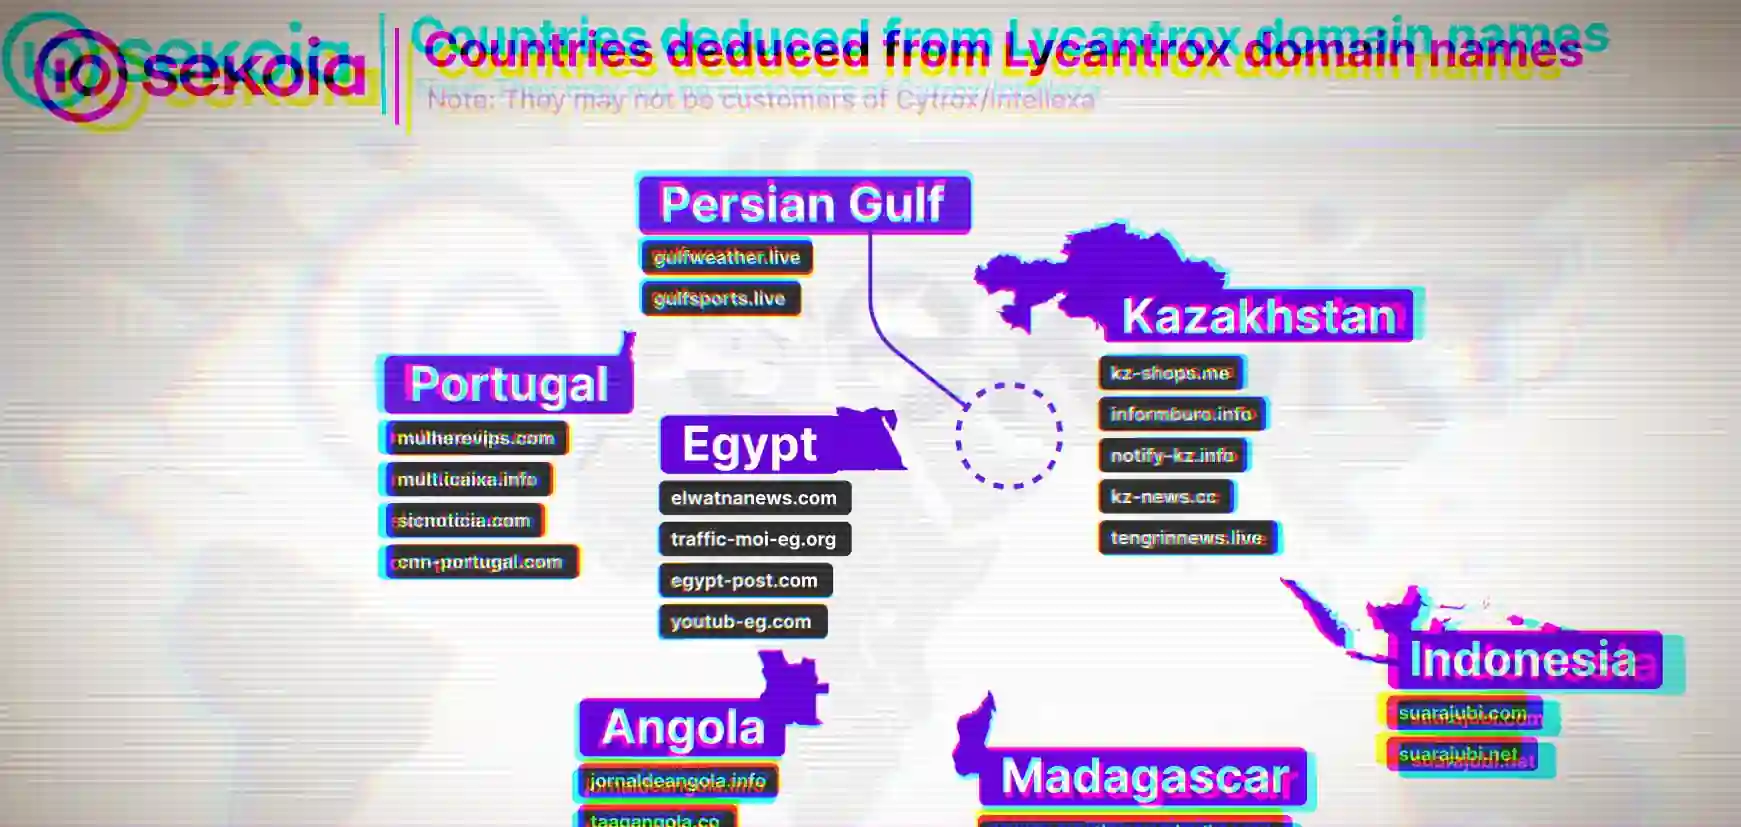
Sekoia.io is actively monitoring hundreds of malicious infrastructure clusters to protect its customers. In light of the recent Citizenlab blogspot and in solidarity with the efforts against cyber mercenaries, we have chosen to shed light on one of t
Sekoia mid-2023 ransomware threat landscape
This blog post aims at presenting an overview of the ransomware-related threat evolution in the first half of 2023. The observations and the analysis shared in this blog post focus on ransomware operations mostly impacting corporate networks in lucra
The transportation sector cyber threat overview
This report aims at contextualising cyber activities targeting the transportation sector worldwide over the 2022 - 2023 period. This report is based on open source reporting and Sekoia.io observations of campaigns mostly impacting the road, air and r

My tea's not cold. An overview of China's cyber threat
This report is an overview of recent malicious cyber activities associated to China-nexus Intrusion Sets. It is based on open-source documents and Sekoia TDR analysts research and does not intend to present an exhaustive list of campaigns.

Engineering detection around Microsoft Defender
This blogpost slightly introduces Microsoft Defender different products and the confusion that can be made between them mainly because they were renamed over the years. Then it focuses on detection engineering around Microsoft Defender Antivirus (MDA
CustomerLoader: A new malware distributing a wide variety of payloads
This blog post aims at presenting a technical analysis of CustomerLoader focusing on the decryption of the next-stage payloads, an overview of more than 30 known and distributed malware families, and details on three infection chains observed distrib

Following NoName057(16) DDoSia Project’s Targets
DDoSia is a Distributed Denial of Service (DDoS) attack toolkit, developed and used by the pro Russia hacktivist nationalist group NoName057(16) against countries critical of the Russian invasion of Ukraine.
Iran Cyber Threat Overview
This blogpost aims at understanding and contextualising cyber malicious activities associated with Iran-nexus intrusions sets over the 2022-2023 period.

Bluenoroff’s RustBucket campaign
In April 2023, fellow security researchers at Jamf published a report on Bluenoroff’s RustBucket, a newly observed malware targeting macOS platform. Sekoia.io analysts further investigated Bluenoroff’s infrastructure and share their findings.

APT28 leverages multiple phishing techniques to target Ukrainian civil society
The APT28 intrusion set (aka. Sofacy, PawnStorm, Fancy Bear), associated to the Russian GRU was observed using multiple phishing techniques to target the Ukrainian civil society.

Overview of the Russian-speaking infostealer ecosystem: The logs
This blog post aims at presenting the life cycle of logs, the cybercrime marketplaces dedicated to logs and the noticeable schemes recently used by threat actors to exploit the stolen data.
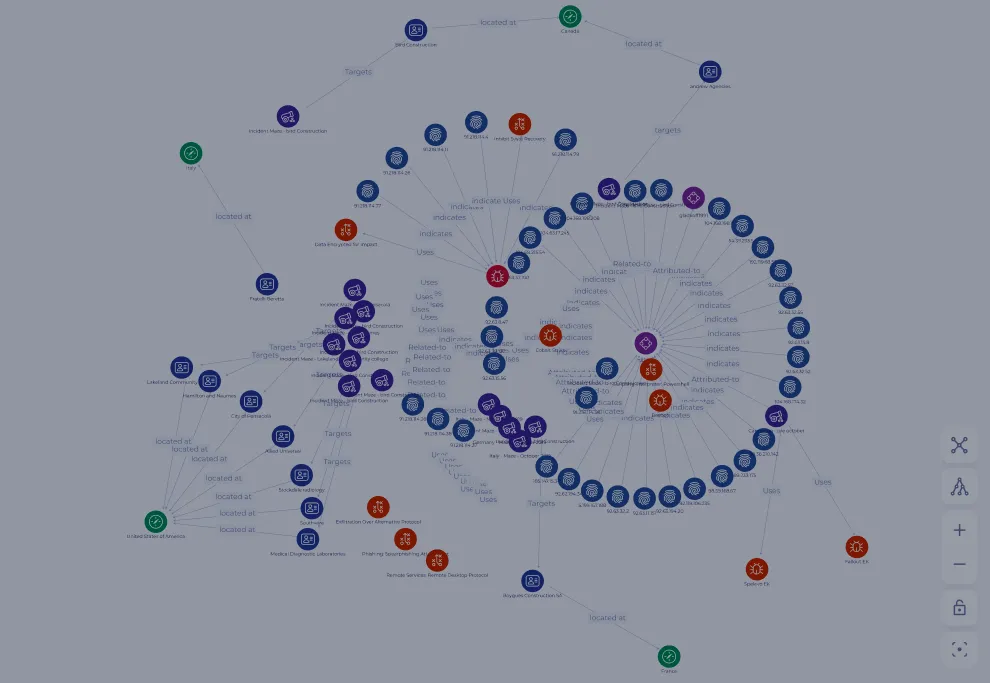
Sekoia CTI at a glance
The CTI produced within Sekoia provides a comprehensive vision on the global cyber-threats alongside technical indicators of compromise (IOC), revealing the presence of attackers. We are in a “one-to-many” model where we are building global intell

Streamline your access with Sekoia's new Single Sign-On (SSO) feature
Sekoia is excited to announce that its Single Sign-On (SSO) feature is now available to all users as a public beta, bringing a host of benefits to streamline your access process.

Russian-speaking infostealer ecosystem: The distribution
This blog post aims at presenting the main techniques, tools and social engineering schemes used by the cybercriminals from the Russian-speaking infostealer ecosystem and observed by Sekoia analysts in the past year.
The energy sector 2022 cyber threat landscape
This report is a joint CITALID and SEKOIA analysis pertaining to cyber activities targeting the energy sector in 2022 in Europe. It is based on open sources reports and includes both our investigations and analysis. Information cut-off date is 22

Sekoia analysis of the #VulkanFiles leak
In January 2023, French newspaper Le Monde offered Sekoia to cooperate on investigating exfiltrated Russian-written documents related to the Moscow-based private company Vulkan.
Threat Detection & Research team
Sekoia Threat Detection & Research team, commonly known as the TDR team, is the driving force behind the Sekoia SOC platform, delivering exclusive threat intelligence.
