

Sekoia Blogs

The Architects of Evasion: a Crypters Threat Landscape
In this report, we introduce key concepts and analyse the different crypter-related activities and the lucrative ecosystem of threat groups leveraging them in malicious campaigns.

NoName057(16)'s DDoSia project: 2024 updates and behavioural shifts
Learn about NoName057(16), a pro-Russian hacktivist group behind Project DDoSia targeting entities supporting Ukraine. Discover an overview of the changes made by the group, both from the perspective of the software shared by the group to generate DD
The Predator spyware ecosystem is not dead: Intellexa's active C2 infrastructure and targeted countries
Discover our TDR team's revelations about Predator spyware: its C2 infrastructure and list of countries still using its cyber espionage tool.
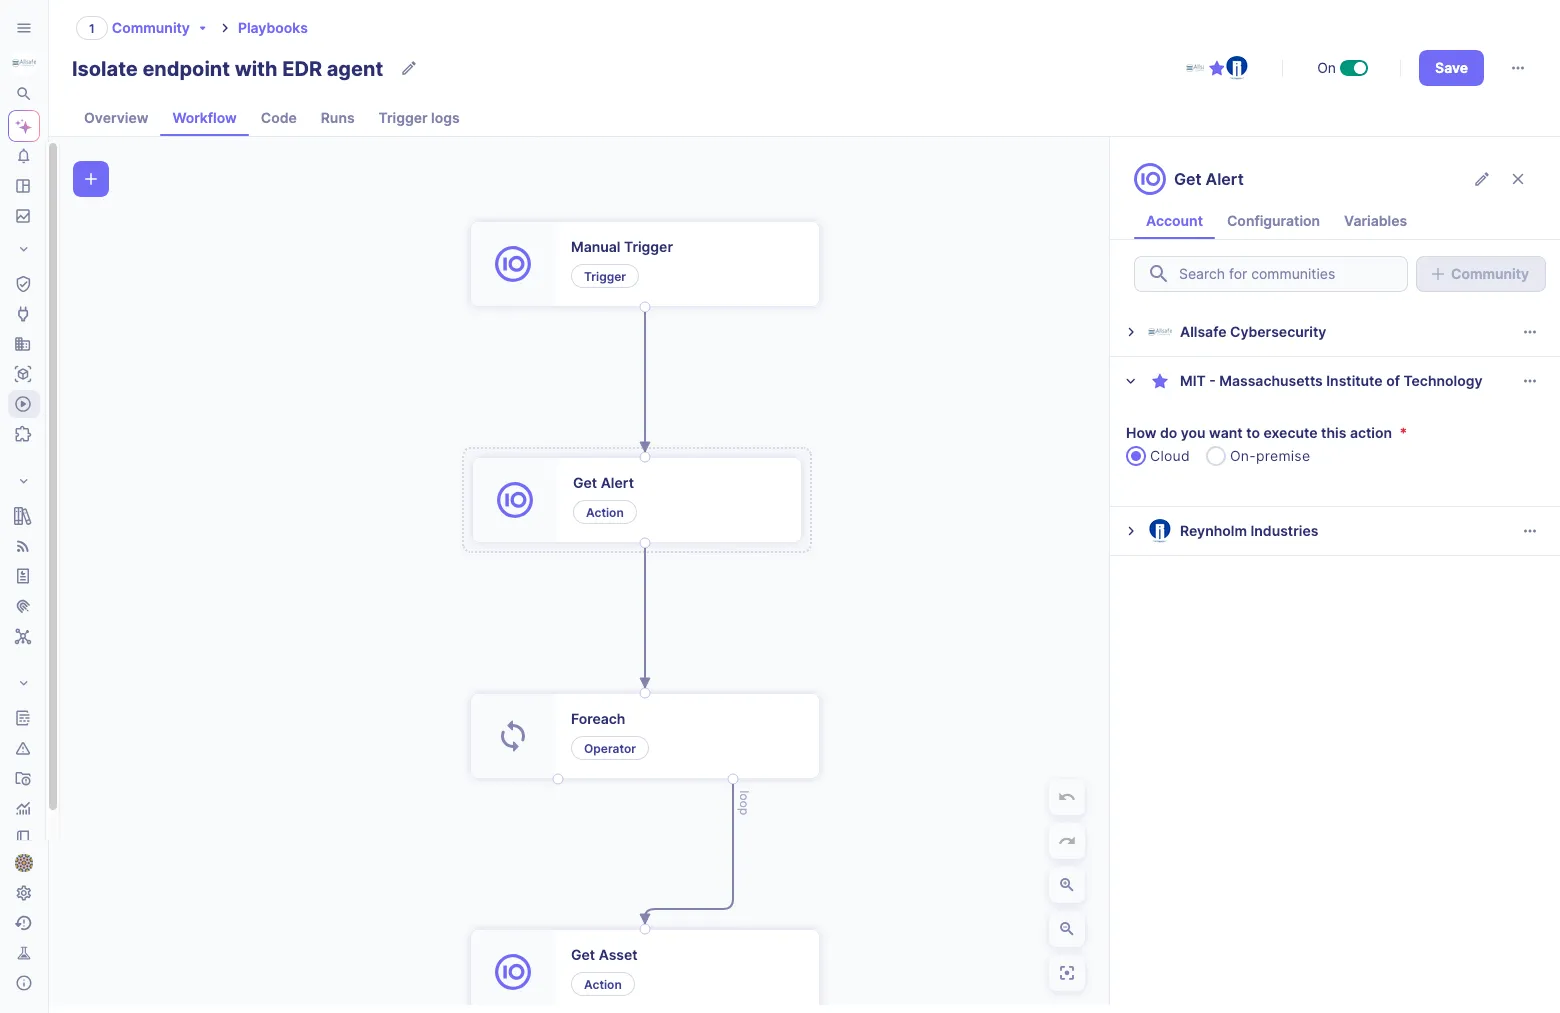
Playbooks on-prem
Playbooks on-prem may appeal to companies seeking to synchronize cloud actions with those executed on-premises.
Scattered Spider (aka UNC3944) Laying New Eggs
This report provides an overview of the Scattered Spider evolution, its modus operandi and the toolset leveraged over the past years. Additionally, it delves into the Scattered Spider TTPs, as well as the latest ongoing campaigns.
How the Sekoia Endpoint Agent works
Explore how Endpoint Agent differs from EDR and collects events to forward logs to Sekoia XDR for in-depth analysis against detection rules.

Adversary infrastructures tracked in 2023
Sekoia.io C2 Trackers identified more than 85,000 IP addresses used as C2 servers in 2023, an increase of more than 30% compared to 2022.
Unveiling the intricacies of DiceLoader
This report aims to detail the functioning of a malware used by FIN7 since 2021, named DiceLoader (also known Icebot), and to provide a comprehensive approach of the threat by detailing the related Techniques and Procedures.
SentinelOne and Sekoia Integration
Sekoia SOC integrates with SentinelOne EDR for robust cybersecurity. Explore threat event detection, playbooks, and automated actions.
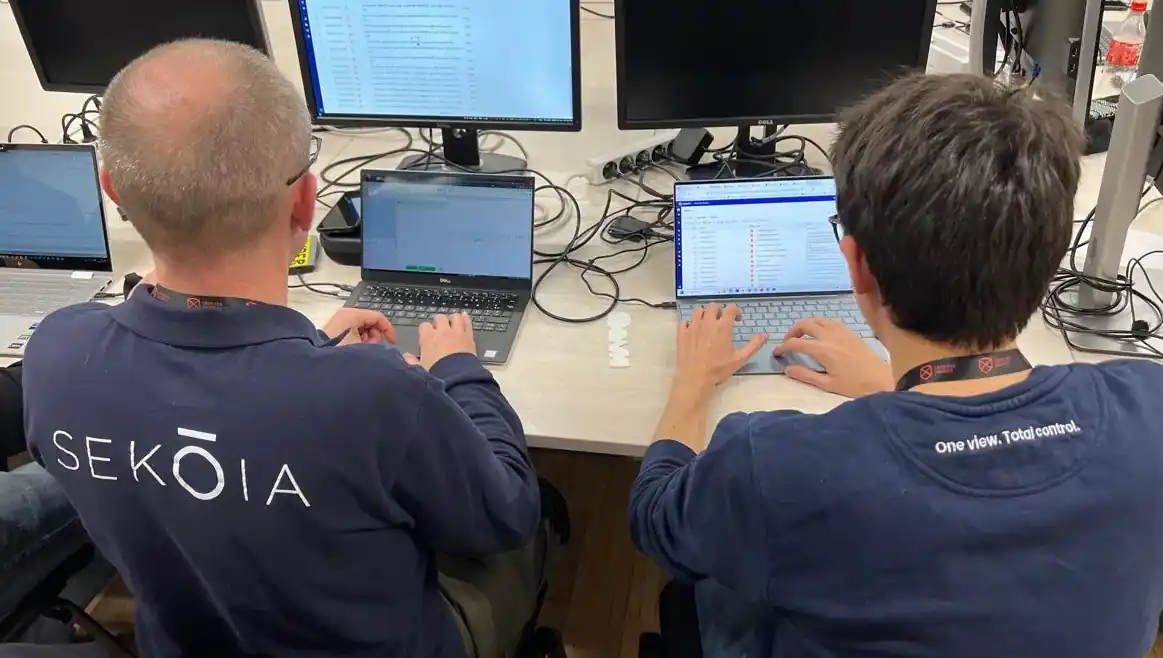
Detecting Berylian attacks: Sekoia SOC Platform used in NATO CCDOE Crossed Swords 2023
Sekoia took part to NATO Cooperative Cyber Defence Centre of Excellence (CCDOE) Crossed Swords cyber exercise organized in Tallinn, Estonia.
Integrating Zscaler ZIA with Sekoia
Integrate Zscaler with Sekoia to streamline incident response and threats detection. Discover how to send Zscaler events to Sekoia.io through NSS or Cloud NSS feeds. Implement a resilient cybersecurity approach!
Being PCI DSS certified
Being PCI certified is a long journey. We started two years ago when we were discussing an extension of our coverage with a customer. This customer was processing card data and consequently had to be partnering with PCI-compliant security solutions t
How Sekoia empowers cybersecurity with 300+ integrations
Sekoia offers 300+ security integrations - Cloud and SaaS, Endpoints, Network, IAM, Threat Intelligence. Explore our integration roadmap.
Securing gold: Assessing cyber threats during Paris 2024
Based on these observations and given the constantly evolving cyber threat landscape, we analysed cyber threats affecting previous editions of the Olympics, as well as the current geopolitical context to understand potential motivations of malicious activity.
IAM & Detection Engineering
Discover the importance of IAM event detection and why it's vital to protecting digital assets from cyber threats.

CALISTO doxxing: Sekoia findings concurs to Reuters’ investigation on FSB-related Andrey Korinets
Discover activities linking Korinets to CALISTO doxxing in our investigation. Uncover details from emails, domains & servers used to target UK Parliament & Cambridge University.
ActiveMQ CVE-2023-46604 exploited by Kinsing: Threat analysis
Discover a technical analysis of the exploitation of the CVE-2023-46604 vulnerability by Kinsing intrusion set.
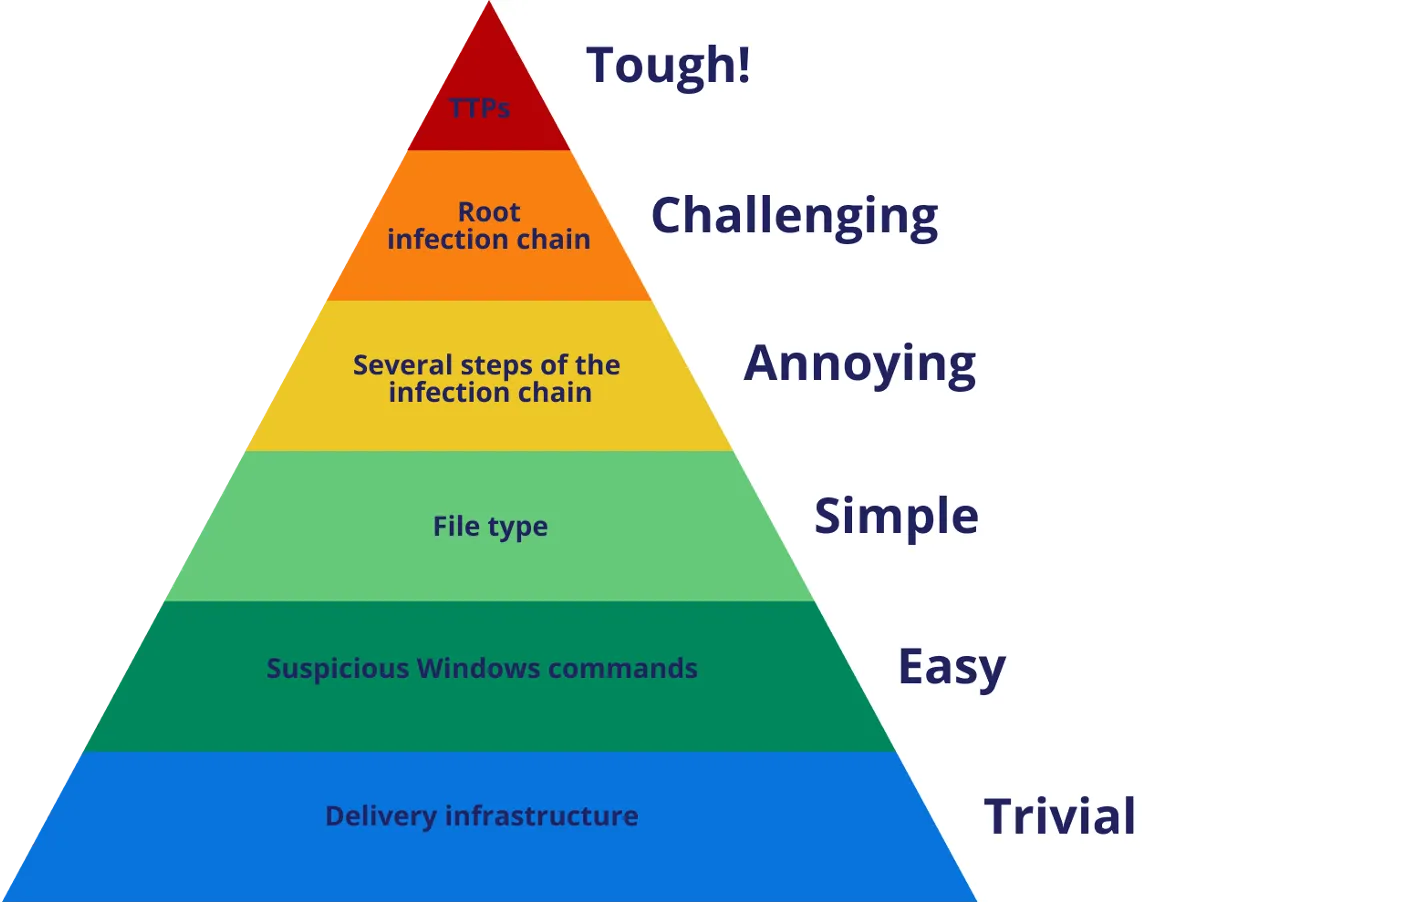
When a botnet cries: Detecting botnet infection chains
Infection chains used by commodity malware are constantly evolving and use various tricks to bypass security measures and/or user awareness. BumbleBee, QNAPWorm, IcedID and Qakbot are all often used as first-stage malicious code.
Sekoia achieves PCI-DSS compliance
Sekoia is proud to announce that it has achieved the Payment Card Industry Data Security Standard (PCI-DSS) compliance at Level 1.
Revolutionize your security strategy: Introducing automatic asset discovery
In the rapidly evolving cybersecurity landscape, staying ahead of potential threats requires a robust and comprehensive approach to managing IT assets. We are pleased to announce the beta release of our newest feature, Asset Discovery,…
Unmasking the latest trends of the financial cyber threat landscape
Financial cyber threat analysis: pinpoint common tactics, techniques & procedures used by intrusion sets to protect the financial system.
Threat Detection & Research team
Sekoia Threat Detection & Research team, commonly known as the TDR team, is the driving force behind the Sekoia SOC platform, delivering exclusive threat intelligence.
