
PHP2Shell was exploited before the patch. Expect more of it.
Attackers exploited PHP2Shell four days before the patch arrived, showing why security teams can no longer wait for disclosure to start investigating.

With Sekoia Intelligence, we gave you half the picture. Here's the other half.
Stolen credentials can pass through several hands before an attacker uses them to access your organization, and each step leaves clues security teams can act on.
Why multi-tenant SOCs need multi-level agents
One SOC can protect dozens of customers, but every customer works differently. See how multi-level agents give security teams one shared way to investigate alerts, while keeping the local context needed to make the right call.
AI SOC agents are only as good as the context they can see
AI SOC agents need more than an alert to investigate threats. See how telemetry, asset data, identities and threat intelligence help explain each verdict.
What you need to know before putting AI agents in your production SOC
A convincing demo doesn’t prove production readiness. Learn how to test an AI agent before it takes on live SOC investigations.
Every detection needs a next step: Why runbooks solve the investigation problem
A detection can raise the alarm and still leave the analyst with the hardest work. Runbooks put the investigation path beside the alert.
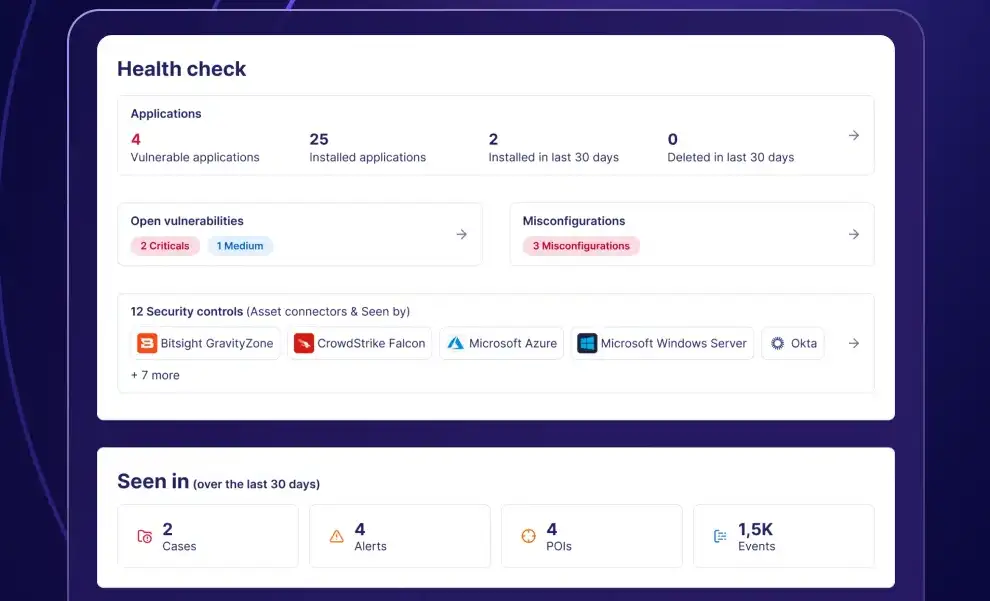
Meet Sekoia Reveal: Turn fragmented asset data into unified SOC context
Security teams do not struggle with a lack of data. They struggle with a lack of context.

UEBA in the Real World: Catching Intrusions That Don’t Look Like Intrusions
Traditional SOC rules miss attacks using valid accounts and MFA fatigue. Learn real-world cases where UEBA detects stealthy lateral movement, OAuth abuse, and cloud console misuse.
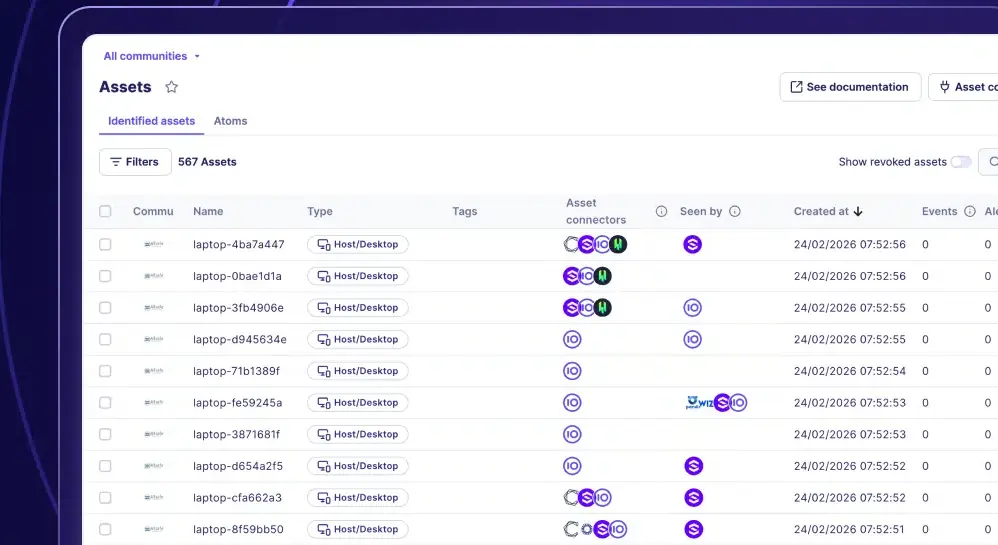
Shadow IT: The Initial Access You Didn’t Log
Shadow IT isn’t just governance debt, it’s an attacker’s beachhead. This post explores real intrusions where forgotten assets, rogue tenants, exposed cloud storage, and abandoned domains enabled initial access, and why closing visibility gaps is now a core SOC capability.

The evolution of the AI SOC: From Hype to Hyper
Explore the impact of Agentic AI in SOC operations and how it boosts efficiency and effectiveness for SOC teams.