Most SOCs do not need another security product.
They need the products they already own to work as one system.
Ask a security team what slows them down and the answers are usually familiar:
- The SIEM takes months to tune.
- Security tools do not share enough context.
- Analysts spend their time moving between consoles.
- Every new integration becomes a project.
- Too much time is spent investigating noise instead of real threats.
For years, the industry responded by adding more tools around the SIEM. That expanded the stack, but not necessarily the team’s ability to detect, investigate and respond.
In March 2026, Gartner published a Market Overview for Integrated Security Operations Center solutions, or ISOC. The research describes ISOC as an emerging approach to bringing threat detection, investigation and response into a more integrated operating model.
The practical questions behind this shift are straightforward: What does ISOC change in practice, and what should buyers look for? This article is my answer.
What is an ISOC, really?
An ISOC is not simply a better SIEM.
It is a different way of delivering security operations.
A traditional SIEM provides a powerful and flexible engine. The customer then builds the SOC around it: connectors, detection rules, threat intelligence, investigation workflows, case management, automation and response.
That model can work. But it also transfers much of the complexity to the customer.
An ISOC takes a different approach. The vendor delivers more of the SOC as an integrated system, with technologies, content and workflows designed to work together from the start.
In practical terms, an ISOC should answer six questions:
- Does it provide the core capabilities of a SIEM? Data ingestion, normalization, monitoring, investigation and reporting, including data from third-party security tools.
- Does it bring the key SOC capabilities into one operating model? SIEM, endpoint detection, threat intelligence and AI-assisted SOC capabilities are among the core components Gartner highlights.
- Can teams manage detection, investigation and response from one place? This includes response actions, automation, playbooks and next-action guidance.
- Is threat intelligence native to the workflow? Intelligence should enrich detections and investigations, not exist as a separate system that analysts have to consult manually.
- Are integrations, detection content and workflows maintained by the vendor? The goal is to reduce the amount of integration work that customers have to build and maintain themselves.
- Do analysts get one cross-product investigation experience? Analysts should be able to connect signals, entities, intelligence and incidents without constantly switching between disconnected tools.
Gartner’s published description includes several additional mandatory capabilities, including a workbench for developing monitoring objectives and vendor-designed cross-product collaboration.
In one sentence:
An ISOC is designed to deliver a working security operations system, not just another box of parts.
What an ISOC is not
It is not just a new user interface placed on top of disconnected products.
It is not an AI chatbot added to a traditional SIEM.
It is not simply an AI agent layered on disconnected telemetry or existing workflows.
It is not necessarily a requirement to replace every security technology already deployed.
The real value lies in how data, intelligence, detection, investigation and response work together as a system.
That distinction matters because security operations are not built from identical components. Most organizations already have an EDR, firewalls, identity tools, cloud services and other technologies they rely on.
Why now?
ISOC is emerging because several problems have become too expensive to ignore.
1. Security operations have become too complex
The challenge is no longer only finding the right security products. It is operating them together.
Every additional platform brings new integrations, data models, detection logic, workflows and maintenance requirements. Complexity eventually becomes an operational risk.
2. Best-of-breed creates hidden costs
Selecting the best tool for every individual capability can look attractive on paper.
But the total cost also includes evaluating vendors, integrating platforms, maintaining connectors, normalizing data, updating detection content and training analysts across multiple interfaces.
The result can be a powerful stack that is difficult to operate consistently.
3. Lean teams cannot build everything from scratch
Many security teams do not have the resources to design and maintain an entire SOC operating model internally.
They need more than raw technology. They need usable content, integrations, investigation guidance and automation that deliver value quickly.
4. Automation needs to support real workflows
Security teams are not looking for automation for its own sake.
They want automation that reduces repetitive work, adds context to alerts, accelerates investigations and helps analysts make better decisions.
AI agents can contribute to this by correlating signals, gathering evidence, enriching alerts and guiding the next step. The objective is not to remove human judgment. It is to make human judgment more effective.
5. Time to value has become a strategic concern
Security leaders are increasingly asking:
- How quickly can we deploy?
- How much tuning will be required?
- How many people will we need to operate the platform?
- How quickly will analysts become productive?
- Can we measure the improvement in investigation and response?
The category is no longer purely theoretical. Microsoft, for example, now documents an ISOC experience in Microsoft Defender that brings together XDR, SIEM, threat intelligence, automation and AI capabilities.
The relevant question for buyers is therefore not simply which platform has the longest feature list.
It is whether the platform improves measurable TDIR (Threat Detection, Investigation and Response) outcomes.
The trade-off: Integration can become lock-in
Gartner makes the trade-off explicit.
Integrated platforms can reduce complexity and provide more value out of the box. But they may also offer less open extensibility than a collection of independent best-of-breed tools. ISOC solutions often rely heavily on vendor-provided integrations, content and workflows.
This raises several questions for CISOs:
- What happens to the EDR already deployed?
- What happens to the firewall and cloud controls that already work?
- What happens to the MSSP and its operating model?
- What happens when the security stack becomes dependent on one hyperscaler?
- What happens if the organization needs to change one component later?
The challenge is then to build an ISOC without turning integration into a closed ecosystem.
Beyond integration
In a recent post, I asked if this was a pivoting moment for our industry. I'm now convinced it is now.
ISOC is a useful lens for understanding the move from fragmented security tools toward a more integrated TDIR operating model.
Ultimately, the important measure will not be the number of capabilities assembled within a platform. It will be the quality of the security outcomes the system enables: faster investigation, better decisions, more effective response and less operational complexity.
And what about Sekoia?
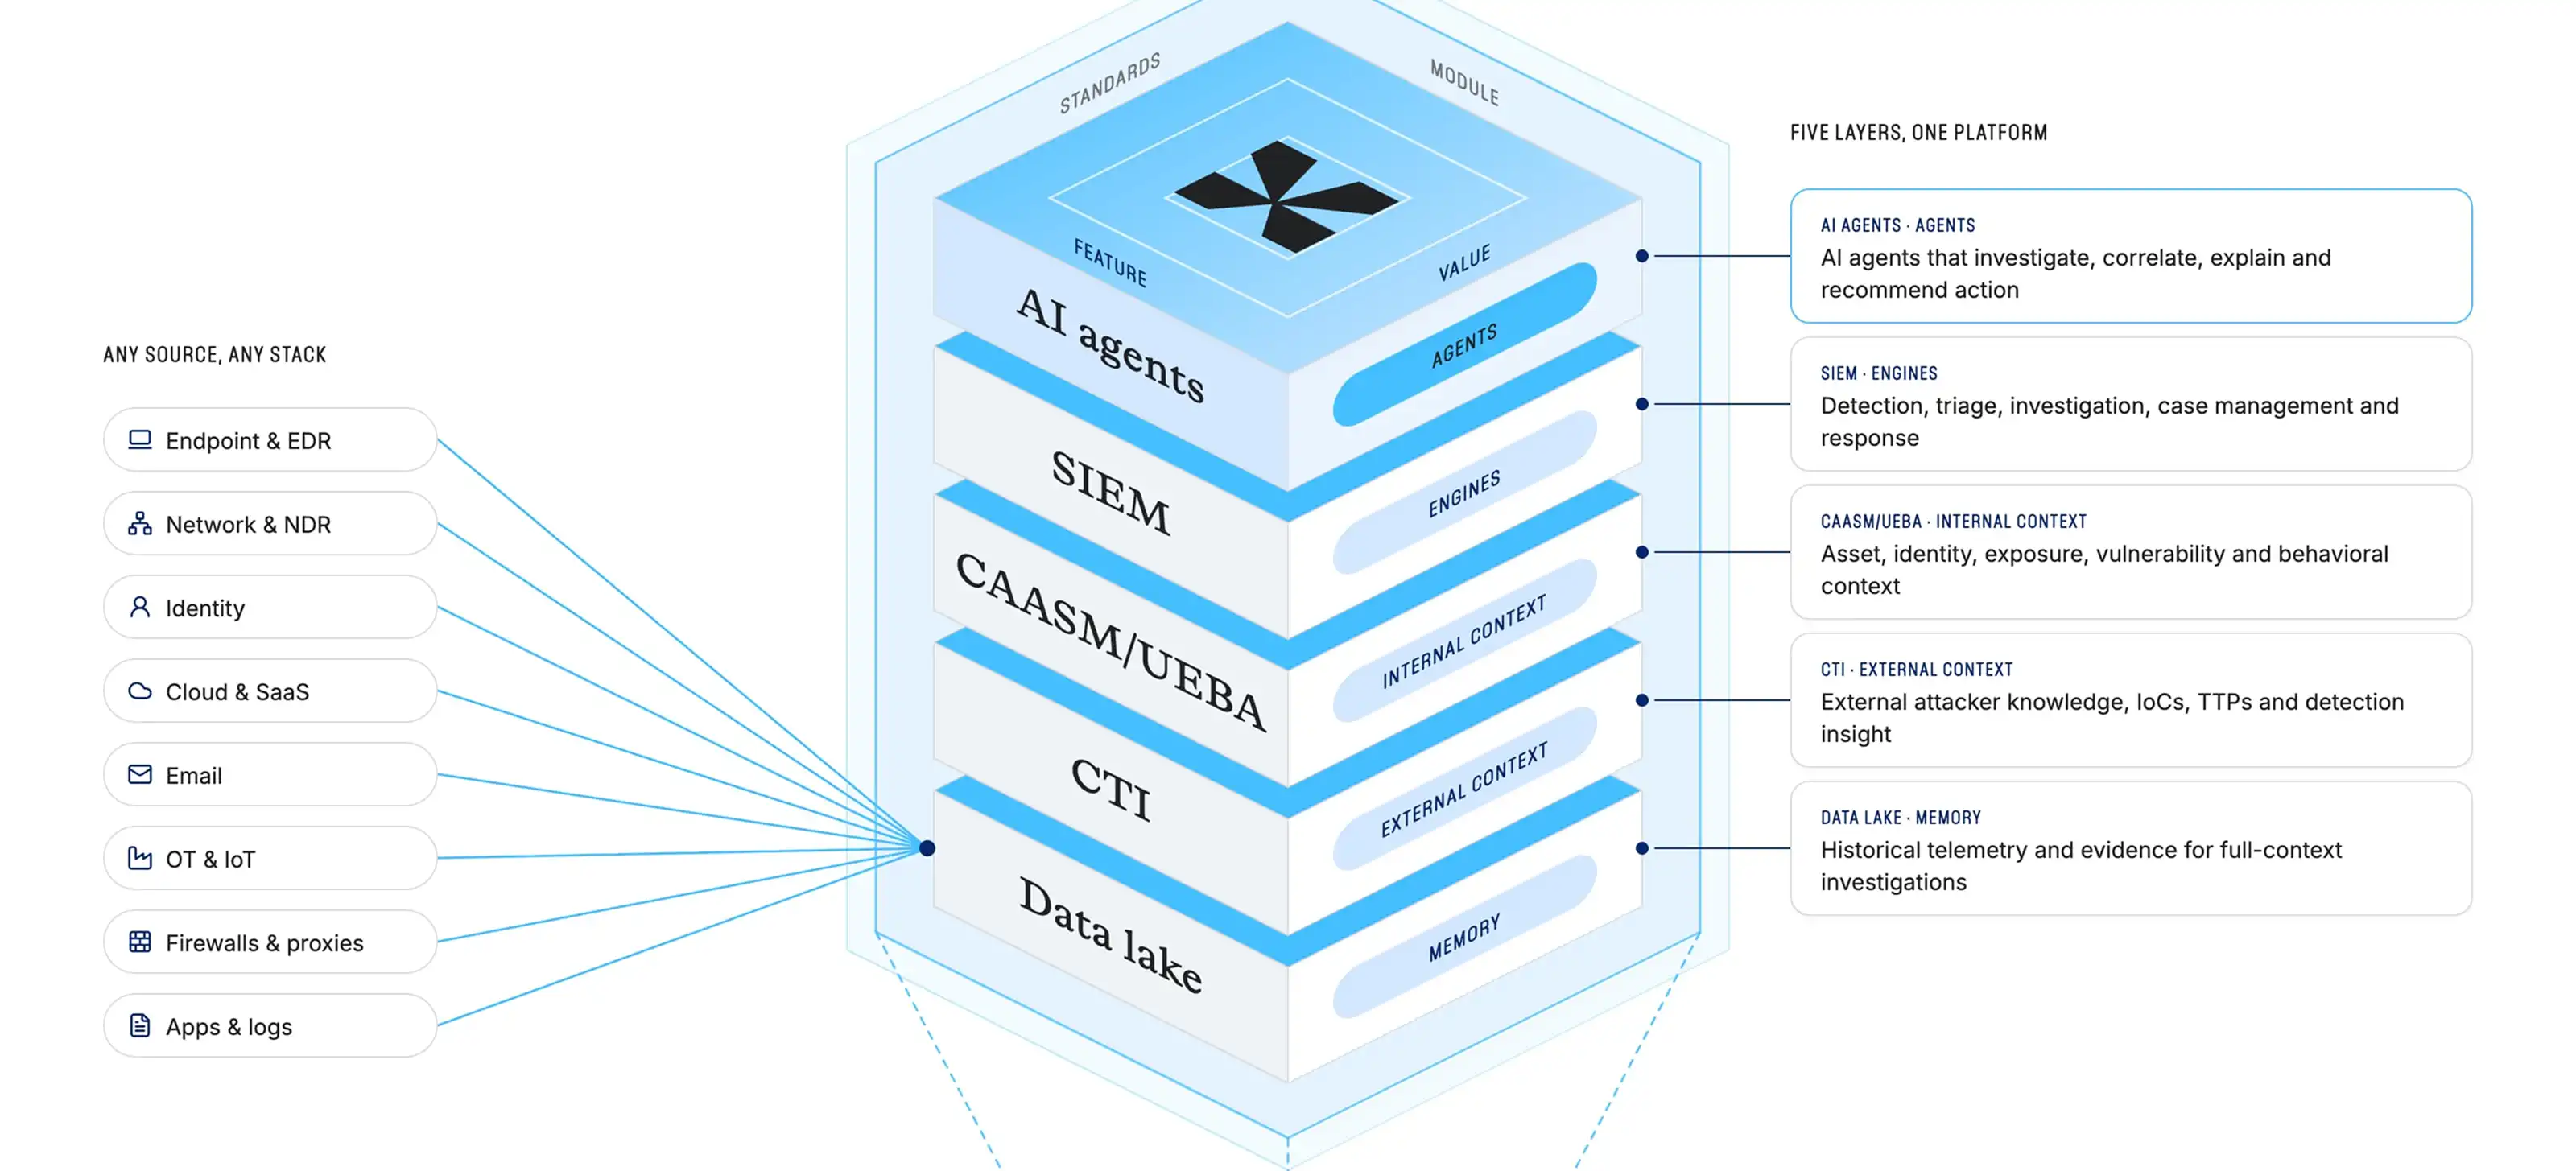
For Sekoia, integration is one part of a broader ambition: building the infrastructure that enables organizations worldwide to evolve toward Autonomous Cyber Defense.
The animation below shows, at a glance, how Sekoia approaches this evolution today. It illustrates an integrated operating model while highlighting two additional dimensions that are important to us:
- Deployment flexibility, from SaaS to self-hosted and air-gapped deployments.
- Operating-model flexibility, supporting enterprise security teams, MDR and MSP providers, tool and API use cases, and emerging MCP-enabled workflows.
Learn more about how Sekoia addresses the core capabilities of integrated security operations by visiting our resource center.